How to Turn Off Windows Defender: Risks, Methods & Expert Insights
Microsoft’s Windows Defender has evolved from a basic security tool into a robust, AI-driven antivirus system integrated into Windows 10 and 11. Yet, despite its improvements, users occasionally seek to disable it—whether for testing third-party antivirus software, troubleshooting conflicts, or specific enterprise policies. The question of how to turn off Windows Defender isn’t just about technical steps; it’s about understanding the trade-offs between convenience and security. Without proper safeguards, disabling this layer of protection can leave systems vulnerable to exploits, ransomware, and zero-day attacks. The decision to disable it should never be taken lightly, especially in environments where data integrity is critical.
The process itself is deceptively simple: a few clicks in the Windows Security app or a registry tweak can render Defender inactive. But the aftermath—potential malware infections, compliance violations, or even system instability—can be far more complex. Many users assume disabling Defender is harmless if they have another antivirus installed, but overlaps or misconfigurations can create blind spots. Enterprise administrators, meanwhile, often disable Defender as part of group policies, only to face audits or security incidents later. The key lies in balancing functionality with risk mitigation, whether through temporary deactivations, scheduled exclusions, or layered security models.
For developers, IT professionals, or even home users running security tests, knowing how to turn off Windows Defender is a necessary skill—but one that demands context. Should you disable it entirely, or merely adjust its settings? What are the hidden consequences of leaving real-time protection off? And how can you re-enable it safely if something goes wrong? This guide cuts through the noise, providing actionable methods, risk assessments, and best practices to ensure you’re informed before making any changes.

The Complete Overview of How to Turn Off Windows Defender
Windows Defender, now rebranded as Microsoft Defender Antivirus, is the default endpoint protection suite for Windows, offering real-time malware scanning, exploit mitigation, and cloud-delivered threat intelligence. Its integration with Windows Update ensures automatic signature updates, but its aggressive scanning can sometimes conflict with performance-heavy applications or enterprise software. Users often turn to disabling it for short-term testing, compatibility fixes, or to comply with third-party antivirus licensing agreements. However, the act of disabling it—even temporarily—requires a structured approach to avoid unintended exposure.The methods to disable Windows Defender vary by Windows version, user permissions, and system configuration. In Windows 11, Microsoft has streamlined the process through the Windows Security app, while older versions rely on Group Policy Editor or Registry tweaks. Each method carries its own implications: Group Policy changes, for instance, can be pushed across entire domains, whereas registry edits are user-specific but risk corruption if mishandled. The choice of method depends on whether you need a quick toggle, a permanent disable, or a conditional exclusion. Understanding these nuances is critical before executing any command, as irreversible changes can compromise system security.
Historical Background and Evolution
Windows Defender’s origins trace back to 2006, when Microsoft released it as a lightweight antivirus for Windows XP and Vista. Initially, it was a minimalist tool designed to complement third-party security suites, but its capabilities expanded with Windows 7, where it became the default antivirus. The shift from a basic scanner to a full-fledged Endpoint Protection Platform (EPP) began with Windows 8, integrating behavioral analysis and cloud-based threat detection. By Windows 10, Defender had matured into a next-generation antivirus (NGAV), leveraging machine learning to detect zero-day threats—a feature that set it apart from traditional signature-based solutions.The evolution of Windows Defender reflects Microsoft’s broader strategy to unify security across its ecosystem. With Windows 11, Defender now includes automatic sample submission to Microsoft’s threat intelligence network, exploit protection controls, and TPM 2.0 integration for hardware-level security. These advancements have made it a formidable defense, but they’ve also increased its resource demands. As a result, users and administrators frequently seek ways to temporarily turn off Windows Defender during software installations, compatibility tests, or when deploying alternative security tools. The historical context underscores why disabling it—without a backup plan—can be risky in modern threat landscapes.
Core Mechanisms: How It Works
At its core, Windows Defender operates through a multi-layered defense system. Real-time protection monitors file executions, network traffic, and system changes, while cloud-delivered protection cross-references local threats against Microsoft’s global threat database. The exploit protection module uses Control Flow Guard (CFG) and Arbitrary Code Guard (ACG) to mitigate memory corruption attacks, a technique borrowed from enterprise-grade security tools. Additionally, offline scanning ensures threats aren’t missed during system reboots, and Windows Sandbox provides an isolated environment for testing suspicious files.Table of Contents
- The Complete Overview of How to Turn Off Windows Defender
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can I permanently disable Windows Defender without uninstalling it?
- Q: Will disabling Windows Defender void my Windows license?
- Q: How do I temporarily disable Windows Defender for a specific task?
- Q: What are the signs that Windows Defender is disabled?
- Q: Is it safe to disable Windows Defender if I have another antivirus?
- Q: How do I re-enable Windows Defender if it’s stuck disabled?
- Q: Does disabling Windows Defender affect Windows Update?
- Q: Can I schedule Windows Defender to disable automatically?
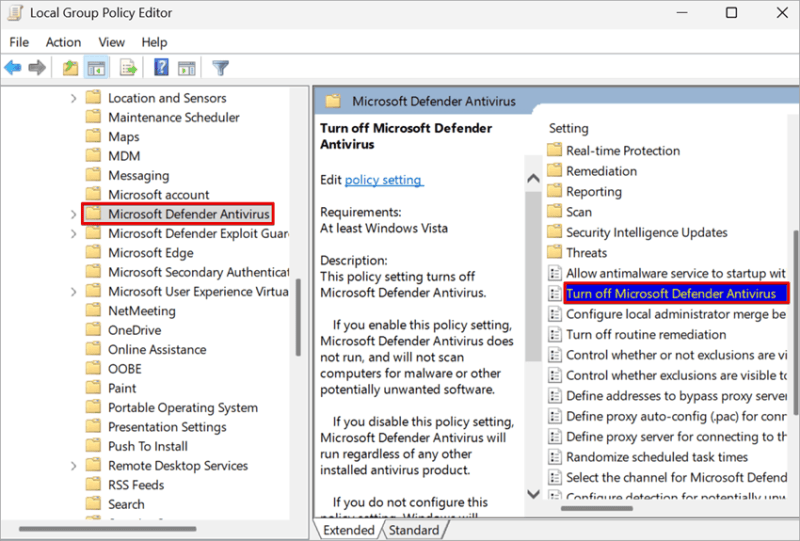
The mechanics behind disabling Defender are equally layered. The Windows Security app provides a GUI-driven method, but under the hood, it modifies registry keys (`HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows Defender\DisableAntiSpyware`) or applies Group Policy settings (`Computer Configuration > Administrative Templates > Windows Components > Microsoft Defender Antivirus`). These changes don’t uninstall Defender but suppress its core functions. For enterprise users, PowerShell commands (`Set-MpPreference -DisableRealtimeMonitoring $true`) offer scriptable control, while Windows Update policies can enforce Defender’s state across managed devices. Understanding these mechanisms is essential to avoid partial disables or misconfigurations that leave systems partially exposed.
Key Benefits and Crucial Impact
Disabling Windows Defender isn’t inherently wrong—it’s often a necessary step in IT workflows. For developers testing security software, it allows for unbiased performance benchmarks without Defender’s interference. Enterprise administrators may disable it to enforce third-party antivirus compliance, especially in regulated industries where specific security suites are mandated. Even home users might temporarily disable Defender to resolve conflicts with gaming overlays or VPN software that trigger false positives. The benefits, however, are outweighed by the risks if not managed carefully.The impact of disabling Defender extends beyond individual machines. In corporate environments, it can violate compliance standards like PCI DSS or HIPAA, leading to audits or fines. For personal users, the consequences might include ransomware infections, data breaches, or botnet recruitment if malware slips through undetected. The balance between functionality and security hinges on risk assessment: Is the temporary disable justified by the task at hand? Are there alternative solutions, such as exclusion rules or scheduled scans, that achieve the same goal without full deactivation?
"Disabling Windows Defender is like turning off a car’s airbag before a high-speed test drive—it might work fine, but one miscalculation could turn a minor issue into a catastrophe." — Microsoft Security Response Center (MSRC)
Major Advantages
Despite the risks, there are legitimate scenarios where disabling Windows Defender is advantageous:- Software Compatibility Testing: Many applications, particularly enterprise software or legacy systems, conflict with Defender’s real-time monitoring. Disabling it temporarily allows for conflict resolution without permanent changes.
- Performance Optimization: Defender’s background scans can consume CPU and RAM, impacting system responsiveness. Disabling it during resource-intensive tasks (e.g., video editing, 3D rendering) can improve performance.
- Third-Party Antivirus Deployment: Some enterprise antivirus suites (e.g., CrowdStrike, SentinelOne) require Defender to be fully disabled to avoid conflicting signatures or double-scanning, which can degrade performance.
- Security Research & Penetration Testing: Ethical hackers and red teams often disable Defender to simulate real-world attack scenarios, testing how systems behave under zero-day exploits.
- Group Policy Enforcement: In Active Directory environments, IT admins may disable Defender via GPOs to enforce corporate security standards or vendor-specific compliance (e.g., IBM Security, Palo Alto).
Comparative Analysis
| Method | Effectiveness | Risk Level | Reversibility ||--------------------------|------------------|----------------|-------------------|
| Windows Security GUI | Temporary (until reboot) | Low (if re-enabled promptly) | High |
| Group Policy Editor | Persistent (domain-wide) | High (enterprise impact) | Medium (requires GPO edit) |
| Registry Tweak | Permanent (until undone) | Medium (registry corruption risk) | Low (manual undo needed) |
| PowerShell Command | Scriptable, remote control | Medium (requires admin rights) | High (revertible via script) |
Future Trends and Innovations
Microsoft continues to refine Windows Defender, with AI-driven threat prediction and automated patch management shaping its future. The integration of Microsoft Defender for Endpoint with Microsoft 365 Defender suggests a shift toward unified security ecosystems, where Defender’s role may expand beyond traditional antivirus into identity protection and cloud threat hunting. For users, this means fewer manual disables will be necessary, as Defender’s adaptive learning reduces false positives and conflicts.However, the demand for how to turn off Windows Defender isn’t likely to disappear. As zero-trust architectures gain traction, organizations will still need to segment security tools, and developers will continue to test software in clean environments. The key innovation will be context-aware disabling—where Defender automatically adjusts its settings based on user role, application type, or network segment, eliminating the need for manual intervention.

Conclusion
The decision to disable Windows Defender should never be impulsive. Whether you’re an IT administrator, a developer, or a home user, the process of turning off Windows Defender requires a clear understanding of the risks, the specific use case, and the safest method to achieve your goal. Temporary disables are less risky than permanent ones, and exclusion rules often provide a middle ground. Always re-enable Defender immediately after completing your task, and consider alternative security layers (e.g., Windows Firewall, BitLocker, or Microsoft Defender for Endpoint) to compensate for its absence.For enterprise environments, documenting the disable and scheduling regular audits can mitigate compliance risks. Home users should ensure they have a reliable third-party antivirus in place before disabling Defender, and developers should test in virtual machines to isolate potential threats. The bottom line: Windows Defender is not just an optional feature—it’s a critical line of defense. Disabling it without necessity is like leaving your front door unlocked; the convenience might be worth it in the short term, but the consequences could be severe.
Comprehensive FAQs
Q: Can I permanently disable Windows Defender without uninstalling it?
No, you cannot uninstall Windows Defender, but you can permanently disable its core features using Group Policy or Registry edits. The service remains installed but inactive. To undo this, revert the changes via the same method (e.g., reset the registry key or modify the GPO). However, Microsoft may re-enable it via Windows Update, so this is not a long-term solution.
Q: Will disabling Windows Defender void my Windows license?
No, disabling Windows Defender does not affect your Windows license. However, corporate licenses (e.g., Windows 10/11 Enterprise) may require Defender to be active for compliance or support validity. Check your Software License Terms if you’re in a managed environment.
Q: How do I temporarily disable Windows Defender for a specific task?
Use Windows Security > Virus & Threat Protection > Manage Settings > Real-time Protection and toggle it off. This change applies immediately but reverts after a reboot. For a non-reboot solution, use PowerShell:
Set-MpPreference -DisableRealtimeMonitoring $true
To re-enable:
Set-MpPreference -DisableRealtimeMonitoring $false
Q: What are the signs that Windows Defender is disabled?
Check the Windows Security app—the Virus & Threat Protection status will show "Off" instead of "On". Alternatively, run:
Get-MpComputerStatus | Select-Object AntivirusEnabled, AntispywareEnabled
If both return False, Defender is disabled. You can also verify via Task Manager (look for the MsMpEng.exe process—if it’s not running, Defender is off).
Q: Is it safe to disable Windows Defender if I have another antivirus?
It can be safe, but only if the third-party antivirus is fully functional and compatible. Overlaps in real-time protection can cause conflicts, performance drops, or missed threats. Best practices:
- Ensure the third-party antivirus is up-to-date and active.
- Use exclusion rules in both Defender and the third-party tool to avoid conflicts.
- Monitor for false negatives (missed malware) during the disable period.
- Re-enable Defender if the third-party antivirus fails or is uninstalled.
Q: How do I re-enable Windows Defender if it’s stuck disabled?
If Defender remains off after a reboot or registry change:
- Open Command Prompt as Admin and run:
sc stop WinDefendsc start WinDefend - Reset the registry key:
reg add "HKLM\SOFTWARE\Microsoft\Windows Defender" /v DisableAntiSpyware /t REG_DWORD /d 0 /f - If using Group Policy, navigate to:
Computer Configuration > Administrative Templates > Windows Components > Microsoft Defender Antivirus > Turn off Microsoft Defender Antivirusand set it to Not Configured. - Run a Windows Update—Microsoft may push a forced re-enable via updates.
Q: Does disabling Windows Defender affect Windows Update?
No, disabling Windows Defender does not block Windows Update. However, security updates (especially those related to exploit mitigations) may still apply, but your system will lack real-time threat detection. Additionally, Windows 11’s TPM 2.0 requirements for security features may prompt Defender to reactivate automatically if certain conditions aren’t met.
Q: Can I schedule Windows Defender to disable automatically?
Yes, using Task Scheduler and PowerShell:
- Open Task Scheduler > Create Task (run as admin).
- Set a trigger (e.g., Daily at 2 AM).
- Under Actions, add a new task:
powershell.exe -Command "Set-MpPreference -DisableRealtimeMonitoring $true" - Create a separate task to re-enable it later (e.g., 30 minutes after disable).
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Bevvy.