Unseen Risks Exposed: Threats Comprehensive Strategies Mitigate Invisible Hazards
The most dangerous threats are the ones you never see coming. While headlines scream about ransomware attacks or geopolitical conflicts, the silent risks—those embedded in supply chains, AI decision-making, or even human psychology—often go unnoticed until it’s too late. These invisible threats thrive in the gaps between firewalls and compliance checklists, exploiting blind spots where traditional defenses fail. The question isn’t if they’ll strike, but when—and whether organizations have the foresight to neutralize them before damage occurs.
Consider the 2017 Equifax breach, where a known vulnerability in unpatched software exposed 147 million records. Or the 2020 SolarWinds supply-chain attack, where a single compromised update infiltrated government and Fortune 500 networks for months. In both cases, the threats weren’t novel; they were comprehensive strategies mitigate invisible risks that slipped through the cracks of reactive security models. The lesson? Visibility alone isn’t enough. Mitigation requires a paradigm shift—one that anticipates the unseen, quantifies the unmeasurable, and acts before the first alert sounds.
Yet most organizations still operate on a detect-and-respond cycle, treating threats as binary events rather than dynamic ecosystems. The reality is far more complex: invisible threats don’t announce themselves with malware signatures or phishing emails. They lurk in strategic blind spots, such as third-party dependencies, algorithmic biases in AI, or the erosion of trust in digital ecosystems. The solution lies in proactive threat mitigation—a discipline that merges behavioral psychology, predictive analytics, and adaptive infrastructure to preempt risks before they materialize.
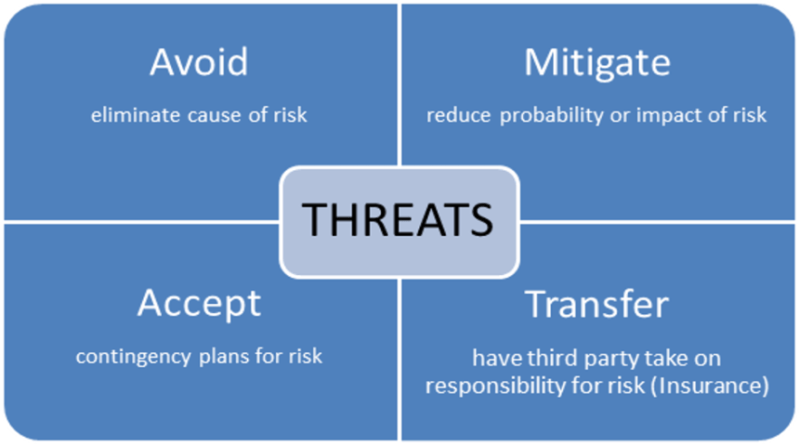
The Complete Overview of Threats Comprehensive Strategies Mitigate Invisible
The concept of mitigating invisible threats isn’t new, but its urgency has surged with the rise of hyper-connected systems, autonomous technologies, and the blurring lines between physical and digital security. Traditional risk management frameworks—rooted in checklists and compliance—were designed to address known, tangible risks. However, the modern threat landscape demands a comprehensive strategy that accounts for unknown unknowns: risks that haven’t occurred yet but are statistically probable, or those that emerge from the interplay of multiple, seemingly unrelated factors. For example, a supply-chain attack isn’t just about a compromised vendor; it’s about the cumulative risk of unmonitored updates, insider negligence, and geopolitical instability converging in a single breach.
Effective mitigation requires three pillars: anticipation (identifying potential threats before they materialize), adaptation (designing systems that can absorb shocks), and resilience (ensuring continuity even when mitigation fails). The goal isn’t to eliminate all risk—an impossible task—but to reduce the invisible threat surface by embedding mitigation into the DNA of operations. This approach is already being adopted by forward-thinking enterprises, governments, and critical infrastructure providers, who recognize that the cost of a single undetected breach can dwarf the investment in preventive measures.
Historical Background and Evolution
The idea of mitigating unseen risks traces back to military strategy, where Sun Tzu’s Art of War emphasized understanding the enemy’s capabilities before engaging. In the digital age, this principle evolved into red teaming and penetration testing, but even these methods often focus on known attack vectors. The shift toward comprehensive strategies for invisible threats gained momentum in the 2010s, as cyber-physical systems (e.g., smart grids, autonomous vehicles) introduced new attack surfaces. The 2015 Ukraine power grid hack—where hackers disabled electricity distribution by manipulating industrial control systems—proved that invisible threats could have physical consequences. Similarly, the 2017 WannaCry ransomware outbreak exposed how a single exploited vulnerability (EternalBlue) could propagate globally in hours, crippling hospitals and logistics networks.
Table of Contents
- The Complete Overview of Threats Comprehensive Strategies Mitigate Invisible
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What are the most common types of invisible threats?
- Q: How can small businesses implement comprehensive invisible threat strategies?
- Q: Are there industries where invisible threat mitigation is more critical?
- Q: Can traditional cybersecurity tools detect invisible threats?
- Q: What’s the biggest misconception about mitigating invisible threats?
- Q: How often should organizations update their invisible threat mitigation strategies?
Academic research further refined the approach. In 2018, the National Institute of Standards and Technology (NIST) published SP 800-37 Rev. 2, emphasizing risk-informed decision-making and the need to address residual risks—those that remain after primary controls are applied. Meanwhile, the financial sector adopted stress testing for cyber risks, simulating worst-case scenarios to identify hidden vulnerabilities. These developments laid the groundwork for modern threat mitigation strategies, which now integrate predictive modeling, behavioral analytics, and adaptive architecture to stay ahead of evolving risks.
Core Mechanisms: How It Works
The most effective comprehensive strategies to mitigate invisible threats operate on three interconnected layers: prevention, detection, and recovery. Prevention begins with threat intelligence fusion, where disparate data sources—dark web monitoring, geopolitical alerts, and internal anomaly detection—are cross-referenced to identify patterns before they manifest. For instance, a sudden spike in lateral movement attempts within a network might indicate a supply-chain compromise, even if no malware has yet been deployed. Detection relies on AI-driven anomaly scoring, which flags deviations from baseline behavior in real time, rather than waiting for predefined signatures. Recovery, the often-overlooked third layer, involves pre-configured playbooks that activate automated responses (e.g., isolating affected systems, rolling back updates) before human intervention is required.
Critical to this framework is the concept of defense in depth with redundancy. Unlike traditional security models that rely on single points of failure (e.g., a single firewall), modern strategies distribute risk across multiple, independent layers. For example, a financial institution might use multi-party computation (MPC) to secure transactions, ensuring no single entity holds the cryptographic keys—thus mitigating the risk of insider threats or key compromise. Similarly, zero-trust architectures assume breach and verify every access request, reducing the attack surface for invisible threats like credential stuffing or pass-the-hash attacks. The key insight is that invisible threats exploit assumptions—assumptions about trust, about predictability, about the invulnerability of certain systems. Mitigation strategies dismantle these assumptions before they can be weaponized.
Key Benefits and Crucial Impact
The transition from reactive to proactive threat mitigation delivers measurable advantages, particularly in sectors where invisible risks can have catastrophic consequences. For healthcare providers, it means avoiding patient data breaches that could disrupt life-saving systems; for energy grids, it prevents blackouts caused by undetected SCADA vulnerabilities; and for financial institutions, it thwarts fraud schemes that exploit gaps in transaction monitoring. Beyond tangible outcomes, these strategies foster organizational resilience, reducing downtime, reputational damage, and regulatory fines. The National Cyber Security Centre (NCSC) estimates that organizations implementing comprehensive invisible threat mitigation experience a 70% reduction in breach-related costs over five years.
Yet the most profound impact lies in strategic agility. Companies that master threats comprehensive strategies mitigate invisible risks can pivot quickly in response to emerging dangers, whether it’s a new ransomware variant or a geopolitical shift that exposes supply-chain dependencies. This agility is a competitive differentiator in an era where disruption is the norm. For instance, a retailer that anticipates AI-driven inventory fraud (where bots manipulate demand signals to trigger over-ordering) can deploy predictive analytics to detect anomalies before they escalate. Similarly, a government agency that models deepfake disinformation campaigns can preempt misinformation before it spreads.
"The greatest threats are not the ones we can see, but the ones we refuse to imagine."
— Eric Symons, Former Director, NSA Cybersecurity Division
Major Advantages
- Proactive Risk Reduction: Identifies and neutralizes threats before they materialize, shifting from a damage-control mindset to prevention-first strategy.
- Cost Efficiency: The average cost of a data breach in 2023 was $4.45 million (IBM). Proactive mitigation reduces this by 60–80% through early intervention.
- Regulatory Compliance: Aligns with frameworks like NIST CSF, ISO 27001, and GDPR, which increasingly demand risk-based security approaches.
- Operational Continuity: Ensures business resilience by maintaining critical functions during zero-day exploits or supply-chain disruptions.
- Competitive Edge: Early adopters gain first-mover advantage in industries where invisible threats (e.g., AI hallucinations, quantum decryption risks) could redefine market dynamics.

Comparative Analysis
| Traditional Risk Management | Comprehensive Invisible Threat Mitigation |
|---|---|
| Focus: Known threats, compliance checklists, reactive responses. | Focus: Unknown/emerging risks, predictive modeling, proactive adaptation. |
| Tools: Firewalls, antivirus, annual audits. | Tools: AI-driven anomaly detection, behavioral analytics, stress testing. |
| Weakness: Relies on historical data; blind to zero-day or supply-chain threats. | Weakness: Requires significant upfront investment in talent and technology. |
| Outcome: Reduces known risks but leaves invisible threats unaddressed. | Outcome: Minimizes unknown unknowns through continuous threat hunting and adaptation. |
Future Trends and Innovations
The next frontier in threats comprehensive strategies mitigate invisible risks lies in quantum-resistant cryptography and AI-native security. As quantum computing advances, classical encryption (e.g., RSA, ECC) will become obsolete, forcing organizations to adopt post-quantum algorithms like lattice-based cryptography. Meanwhile, generative AI is being weaponized to create hyper-realistic phishing campaigns or deepfake audio/video for social engineering. The response? AI vs. AI defense systems that use adversarial machine learning to outmaneuver automated attacks. Another emerging trend is biometric behavioral analysis, where systems monitor how users interact with devices (e.g., typing speed, mouse movements) to detect compromised accounts before credentials are stolen.
Regulatory bodies are also evolving. The EU’s NIS2 Directive and U.S. Cybersecurity Executive Order now mandate risk-based cybersecurity, pushing organizations to adopt comprehensive invisible threat mitigation as a baseline. Meanwhile, insurtech is developing parametric cyber insurance, where payouts trigger automatically based on predefined risk metrics—further incentivizing proactive strategies. The future will likely see autonomous security orchestration, where AI-driven systems not only detect threats but also reconfigure infrastructure in real time to neutralize them, reducing human latency in critical decisions.

Conclusion
The invisible threats of today are the strategic blind spots of tomorrow. Organizations that treat risk mitigation as a static process—checking boxes on a compliance sheet—will find themselves ill-prepared when the next undetected breach occurs. The alternative? A dynamic, adaptive framework that treats threats comprehensive strategies mitigate invisible risks as an ongoing dialogue between threat actors and defenders. This requires cross-disciplinary collaboration (merging cybersecurity, data science, and operational resilience), continuous investment in emerging technologies, and a cultural shift toward anticipatory thinking.
The good news is that the tools and methodologies already exist. The challenge is implementing them before the next invisible threat becomes visible—and too late. The organizations that succeed will be those that recognize mitigation isn’t just about stopping attacks; it’s about redefining the boundaries of the possible before adversaries can cross them.
Comprehensive FAQs
Q: What are the most common types of invisible threats?
A: Invisible threats typically fall into five categories:
- Supply-Chain Risks: Compromised third-party software/hardware (e.g., SolarWinds, Kaseya ransomware).
- AI/ML Exploits: Adversarial attacks on machine learning models (e.g., poisoned training data, model inversion attacks).
- Human-Centric Vulnerabilities: Insider threats, social engineering (e.g., deepfake CEO fraud), or fatigue-based errors in high-stress environments.
- Systemic Gaps: Misconfigured cloud storage, default credentials, or unpatched legacy systems.
- Emerging Tech Risks: Quantum decryption threats, IoT botnet hijackings, or 5G network exploits.
Q: How can small businesses implement comprehensive invisible threat strategies?
A: Small businesses should start with:
- Threat Modeling: Map critical assets and identify how they could be exploited (e.g., via STRIDE framework).
- Third-Party Risk Assessments: Audit vendors for supply-chain vulnerabilities (tools like BitSight or SecurityScorecard can help).
- Behavioral Analytics: Deploy UEBA (User and Entity Behavior Analytics) to detect anomalies (e.g., Microsoft Defender for Identity).
- Automated Patching: Use solutions like Patch Management (e.g., Tanium) to close known gaps.
- Tabletop Exercises: Simulate zero-day or supply-chain attack scenarios to test response plans.
Q: Are there industries where invisible threat mitigation is more critical?
A: Yes. Industries with high stakes and low tolerance for failure are most vulnerable:
- Critical Infrastructure: Energy grids, water treatment, and transportation (targeted by state-sponsored actors).
- Healthcare: Patient data breaches and medical device hijackings (e.g., Stuxnet precedent).
- Finance: AI-driven fraud and supply-chain payment fraud (e.g., Business Email Compromise).
- Defense/Aerospace: IP theft via insiders or 3D-printed component sabotage.
- Retail/E-Commerce: Inventory fraud (e.g., promotional abuse via bots).
Q: Can traditional cybersecurity tools detect invisible threats?
A: Traditional tools (e.g., SIEMs, EDRs) are signature-based and struggle with unknown threats. However, when combined with:
- AI/ML Anomaly Detection: Tools like Darktrace or Exabeam identify deviations from baseline behavior.
- Threat Intelligence Feeds: Platforms like Recorded Future or Mandiant Threat Intelligence surface emerging risks.
- Red Teaming: Simulated attacks to uncover unpatched blind spots.
Q: What’s the biggest misconception about mitigating invisible threats?
A: The myth that perfection is possible. Many organizations believe they can eliminate invisible threats entirely, leading to analysis paralysis or over-reliance on unproven solutions. In reality, the goal is risk reduction, not eradication. The most successful strategies focus on:
- Acceptable Risk Levels: Defining what risks to tolerate (e.g., risk appetite statements).
- Continuous Improvement: Treating mitigation as a feedback loop, not a one-time project.
- Cultural Buy-In: Ensuring leadership and employees own the process, not just IT teams.
Q: How often should organizations update their invisible threat mitigation strategies?
A: At least quarterly, with real-time adjustments for high-risk events (e.g., new zero-days, geopolitical tensions). Key triggers for updates include:
- Threat Landscape Shifts: Emergence of new attack vectors (e.g., AI-powered phishing).
- Regulatory Changes: Updates to NIST, ISO, or sector-specific guidelines.
- Incident Retrospectives: Post-mortems of near-misses or breaches.
- Technology Advancements: Adoption of quantum computing or edge AI.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Bevvy.