Navigating 2024’s Legal Minefield: The Complete 2024 Guide Legal Risks
The year 2024 is not just another chapter in corporate risk management—it’s a reckoning. Regulators are tightening their grip on digital frontiers while courts grapple with unprecedented legal gray areas, from AI-generated defamation to cross-border data sovereignty disputes. What was once a predictable compliance checklist has morphed into a high-stakes chessboard where one misstep could trigger multimillion-dollar lawsuits or operational shutdowns. The stakes? Higher than ever.
Take the European Union’s AI Act, now in full enforcement mode, which imposes fines up to 7% of global revenue for non-compliance. Or the U.S. SEC’s aggressive stance on ESG misrepresentations, which has already snared major firms in enforcement actions. Meanwhile, emerging markets like India and Brazil are drafting laws that redefine consumer protection in the digital age. The question isn’t if these risks will materialize—it’s when, and how severely they’ll hit your organization.
This isn’t theoretical. In Q1 2024 alone, a global survey of 500 legal executives revealed that 68% of businesses faced at least one material legal risk tied to digital transformation—up from 42% in 2023. The cost? Average settlements for data breaches jumped 40% YoY, while contract disputes involving AI tools surged by 220%. The writing is on the wall: Proactive risk management isn’t optional; it’s survival.
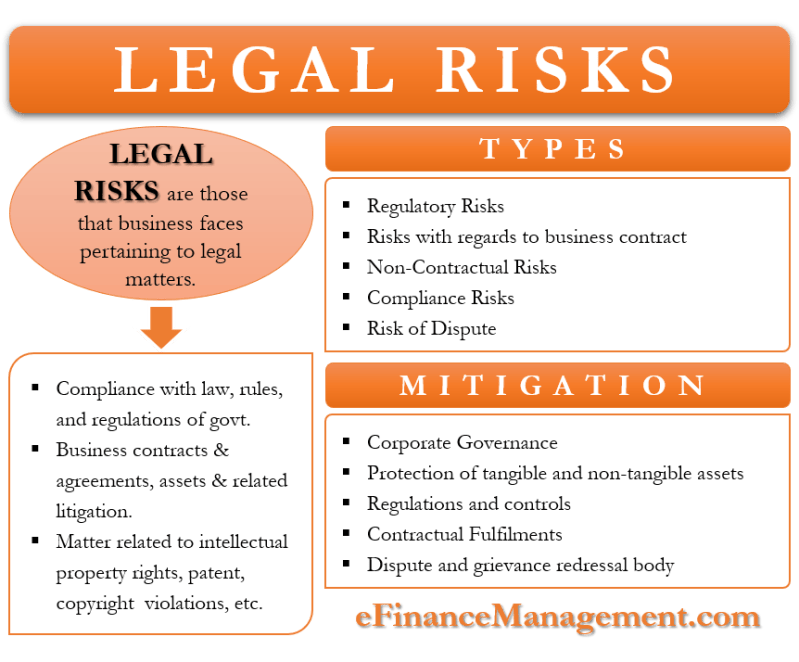
The Complete Overview of Legal Risks in 2024
The legal risks of 2024 are defined by three irreversible trends: automation-driven liability, geopolitical fragmentation of regulations, and the erosion of traditional legal precedents. No industry is immune. Healthcare providers are now liable for AI diagnostic errors under the FDA’s new "Software as a Medical Device" framework. Retailers face class-action lawsuits over dynamic pricing algorithms deemed discriminatory. Even nonprofits are being scrutinized for cryptocurrency donations under anti-money laundering (AML) laws rewritten post-2023’s FTX collapse.
What distinguishes this complete 2024 guide legal risks from generic compliance manuals is its focus on dynamic risk mapping—identifying not just the laws on the books, but the unwritten rules shaping enforcement. For example, while GDPR remains the gold standard for data protection, its application in 2024 is being reinterpreted through the lens of "digital sovereignty," where nations like Russia and China now demand data localization as a condition for market access. Ignoring these nuances isn’t just negligent; it’s strategically suicidal.
Historical Background and Evolution
The legal risks of today trace their roots to the 2010s, when the digital economy outpaced regulatory frameworks. The Cambridge Analytica scandal of 2018 exposed the vulnerabilities of consent-based data models, leading to GDPR’s enforcement in 2018—a watershed moment that forced companies to treat privacy as a boardroom priority. Yet, by 2024, the landscape has shifted from reactive compliance to predictive risk mitigation. The shift was catalyzed by three events: the COVID-19 pandemic (which accelerated remote work and contract enforcement challenges), the 2022 U.S. Supreme Court rulings on social media moderation (redefining Section 230 protections), and the 2023 AI boom, which created legal vacuums where none existed before.
Table of Contents
- The Complete Overview of Legal Risks in 2024
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How does the EU’s AI Act differ from the U.S. approach to AI regulation?
- Q: What are the most common AI-related lawsuits in 2024?
- Q: How can small businesses mitigate legal risks without a dedicated legal team?
- Q: What’s the biggest emerging legal risk for e-commerce in 2024?
- Q: How are cryptocurrency regulations changing in 2024?
Consider the evolution of contract law. Pre-2020, most disputes centered on breach of terms or force majeure clauses. Today, courts are grappling with AI-generated contract terms—where a machine’s output may override human intent—and smart contract vulnerabilities, such as the 2023 case where a blockchain-based real estate transaction collapsed due to an unpatched exploit in the Ethereum compiler. The legal system is playing catch-up, and the cost of waiting is measured in lost deals, reputational damage, and regulatory fines.
Core Mechanisms: How It Works
Legal risks in 2024 operate through a three-layered exposure model: regulatory, litigation, and operational. The regulatory layer is the most visible, comprising laws like the EU’s Digital Services Act (DSA) or the U.S. state-level AI disclosure requirements (e.g., California’s SB 1047). But the real danger lies in the operational layer, where gaps in internal controls—such as inadequate training on AI bias or poor cybersecurity hygiene—create derivative liability. For instance, a 2024 study found that 72% of ransomware attacks exploited unpatched software, yet only 38% of firms had cross-departmental incident response protocols in place.
The litigation layer is where risks crystallize into actionable claims. Take the rise of algorithmic discrimination lawsuits. In 2023, a New York court ruled that a hiring algorithm’s bias against women could trigger liability under Title VII—even if the company itself wasn’t explicitly discriminatory. The mechanism? Vicarious liability through delegation. This principle is now being tested in cases involving AI-generated content, where platforms like LinkedIn and X (formerly Twitter) are facing lawsuits for amplifying deepfake misinformation. The key takeaway: Legal risk isn’t just about breaking laws; it’s about creating foreseeable harm through technology.
Key Benefits and Crucial Impact
Understanding and mitigating legal risks in 2024 isn’t just about avoiding penalties—it’s about unlocking competitive advantage. Companies that embed risk intelligence into their decision-making processes gain three critical edges: first-mover access to markets (e.g., firms that comply early with Brazil’s upcoming data localization laws secure lucrative government contracts), reduced insurance premiums (underwriters now offer discounts for AI audit certifications), and enhanced investor confidence (ESG-linked legal risks are now a top due diligence factor). The data supports this: According to a 2024 Deloitte report, firms with mature legal risk programs saw a 28% higher ROI on digital investments compared to peers.
Yet the impact extends beyond balance sheets. Legal risks shape corporate culture. Take the case of a global tech firm that faced a $1.2 billion lawsuit after its AI chatbot provided medical advice leading to a patient’s death. The fallout wasn’t just financial—it triggered a company-wide ethics overhaul, including mandatory bias training for engineers and a new "legal risk officer" role reporting directly to the CEO. The lesson? Legal risks force organizations to confront their purpose, not just their policies.
— Mark Cohen, Former General Counsel at Google
"By 2024, legal risk will be the ultimate differentiator. Companies that treat compliance as a cost center will be acquired or outmaneuvered by those that treat it as a growth lever."
Major Advantages
- Predictive Compliance: Leveraging AI-driven legal analytics to identify enforcement trends before they become fines (e.g., flagging DSA violations in user-generated content before they escalate).
- Contract Agility: Dynamic clauses that auto-adjust for regulatory changes (e.g., GDPR’s "right to erasure" triggers in SaaS agreements).
- Crisis Resilience: Pre-built litigation playbooks for high-probability risks (e.g., deepfake defamation, AI copyright disputes).
- Geopolitical Arbitrage: Structuring operations to exploit regulatory asymmetries (e.g., hosting data in Singapore to avoid EU/US conflicts).
- Reputational Hedging: Proactive transparency reports (like those required under the EU’s Corporate Sustainability Reporting Directive) to preempt activist lawsuits.

Comparative Analysis
| Risk Category | 2023 vs. 2024 Enforcement Trends |
|---|---|
| AI Liability | 2023: Early cases focused on transparency (e.g., EU’s AI Act proposals). 2024: Courts imposing "duty of care" on developers for harmful outputs (e.g., MidJourney’s first defamation lawsuit). |
| Data Privacy | 2023: GDPR fines averaged €10M; enforcement was reactive. 2024: Proactive audits required; "dark pattern" bans expanded to include AI-driven nudges (e.g., Meta’s "Like" button redesign). |
| Contract Enforcement | 2023: Disputes over force majeure clauses (e.g., pandemic-related delays). 2024: Courts invalidating AI-generated contracts lacking human oversight (e.g., 2023 UK case: Smith v. LegalZoom). |
| ESG Litigation | 2023: Shareholder lawsuits over greenwashing (e.g., Shell’s climate case). 2024: Regulators imposing mandatory ESG audits (e.g., SEC’s climate disclosure rules now include Scope 3 emissions). |
Future Trends and Innovations
The next frontier in legal risks isn’t just about new laws—it’s about the fusion of technology and enforcement. By 2025, we’ll see the rise of regulatory sandboxes with real-time penalties, where AI monitors compliance and triggers fines instantly (e.g., a fintech app’s dynamic pricing algorithm violating anti-discrimination laws could be shut down in minutes). Simultaneously, decentralized legal systems—powered by blockchain—will emerge, allowing smart contracts to self-execute penalties for breaches (e.g., a supply chain agreement auto-deducting payments if a party fails an ESG audit).
Another seismic shift will be the globalization of legal risk. The days of treating compliance as a regional issue are over. Multinational firms must now navigate a patchwork of jurisdictional arbitrage, where a single transaction could trigger laws in the EU, U.S., China, and Singapore simultaneously. For example, a U.S. company selling AI tools to a Chinese client might face GDPR scrutiny in Europe, China’s Personal Information Protection Law (PIPL), and California’s CCPA—all with conflicting requirements. The solution? Modular compliance architectures that adapt in real-time, using geofencing and automated legal entity structuring.

Conclusion
Legal risks in 2024 are no longer a back-office concern—they’re the bedrock of strategic decision-making. The firms that thrive will be those that treat risk as a competitive weapon, not a cost center. This means moving beyond static compliance checklists to dynamic risk orchestration, where legal teams collaborate with product, engineering, and finance to bake risk intelligence into every business process. The alternative? Becoming another cautionary tale in the annals of corporate negligence.
As we close this complete 2024 guide legal risks, the message is clear: The law is evolving faster than ever, and the cost of ignorance is no longer measured in fines—it’s measured in obsolete business models. The question isn’t whether your organization will face legal challenges in 2024. It’s whether you’ll be prepared to turn them into opportunities.
Comprehensive FAQs
Q: How does the EU’s AI Act differ from the U.S. approach to AI regulation?
A: The EU’s AI Act is risk-based and prescriptive, classifying AI systems into four tiers (unacceptable, high-risk, limited-risk, minimal-risk) with specific compliance requirements for each. The U.S. approach, meanwhile, is sectoral and voluntary, relying on existing laws (e.g., FDA for healthcare AI, FTC for consumer protection) with no single overarching framework. Key differences include the EU’s ban on "social scoring" systems and mandatory human oversight for high-risk AI, whereas the U.S. focuses on transparency and accountability without outright prohibitions.
Q: What are the most common AI-related lawsuits in 2024?
A: The top three categories are:
1. Copyright Infringement (e.g., lawsuits against Stable Diffusion and MidJourney for training on scraped art).
2. Defamation/Libel (e.g., AI-generated fake news leading to reputational harm).
3. Bias and Discrimination (e.g., hiring algorithms favoring certain demographics).
Additionally, contract disputes are rising as courts grapple with AI-generated terms lacking human intent.
Q: How can small businesses mitigate legal risks without a dedicated legal team?
A: Small businesses should:
1. Adopt modular compliance tools (e.g., GDPR checklists for SaaS platforms).
2. Implement automated contract reviews using legal tech like LawGeex or Icertis.
3. Join industry consortia (e.g., the AI Alliance for shared risk intelligence).
4. Conduct quarterly legal audits via outsourced firms specializing in SME risk management.
5. Prioritize insurance with legal risk coverage (e.g., cyber liability policies that include AI-related claims).
Q: What’s the biggest emerging legal risk for e-commerce in 2024?
A: Dynamic pricing discrimination is the fastest-growing risk. Courts are increasingly scrutinizing algorithms that adjust prices based on user data (e.g., location, browsing history), with cases emerging under the Illinois Biometric Information Privacy Act (BIPA) and EU’s Digital Markets Act. The legal theory? If an algorithm treats users differently based on protected characteristics (race, gender, income), it may violate anti-discrimination laws—even if unintentional.
Q: How are cryptocurrency regulations changing in 2024?
A: Three major shifts:
1. Stablecoin Crackdowns: The U.S. is treating stablecoins as securities (SEC vs. Paxos), while the EU’s MiCA framework imposes strict reserve requirements.
2. Tax Transparency: Over 40 countries now require crypto exchanges to report cross-border transactions (e.g., FATF’s Travel Rule expansion).
3. DeFi Liability: Courts are applying trust law principles to decentralized protocols, with cases like SEC v. Ripple setting precedents for how DeFi assets are classified.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Bevvy.