How Docker Containers Revolutionized Software Deployment
The first time a developer ran a command to spin up a docker container and watched their application execute in complete isolation—without dependency conflicts or environment mismatches—they experienced a paradigm shift. This wasn’t just another tool; it was a fundamental rethinking of how software is packaged, distributed, and deployed. The docker container emerged not as a solution to a single problem, but as a response to the cumulative frustrations of traditional deployment workflows: bloated virtual machines, inconsistent environments, and the endless "works on my machine" debug sessions.
What followed was a quiet revolution. Companies that had spent years perfecting their CI/CD pipelines suddenly found those pipelines moving at warp speed. Startups could launch products in weeks instead of months. Legacy enterprises, once paralyzed by monolithic architectures, began experimenting with microservices—all because a docker container could encapsulate an entire runtime environment, down to the last library version, in a single, portable artifact. The technology didn’t just optimize workflows; it democratized infrastructure, turning developers into architects of their own deployment ecosystems.
Yet for all its ubiquity, the docker container remains misunderstood. Many treat it as a black box—something that "just works"—without grasping how it dismantles the traditional boundaries between development and operations. The truth is more nuanced: it’s not merely containerization, but a reimagining of the operating system’s isolation mechanisms, repurposed for the cloud era.
The Complete Overview of Docker Containers
At its core, a docker container is a lightweight, standalone, executable software package that includes everything needed to run a piece of code: the application itself, its dependencies, libraries, and configuration files. Unlike virtual machines (VMs), which require an entire guest operating system, docker containers share the host OS kernel, making them far more efficient in terms of resource usage and startup time. This efficiency is the reason why docker containers have become the backbone of modern cloud-native applications, enabling developers to deploy consistent environments across development, testing, and production.The power of docker containers lies in their ability to abstract away infrastructure complexity. A developer writing Python code in their local environment can package it into a docker container and know, with near-certainty, that it will behave identically when deployed to a remote server or a Kubernetes cluster. This consistency eliminates the "it works here but not there" syndrome that has plagued software teams for decades. The docker container doesn’t just run code—it guarantees the context in which that code runs, making it a cornerstone of reproducible builds and DevOps practices.
Historical Background and Evolution
The origins of docker containers can be traced back to 2008, when Google engineers developed a project called LXC (Linux Containers) to improve the efficiency of their data centers. While LXC provided process and resource isolation, it lacked the user-friendly interface and ecosystem that would later define docker containers. Enter Docker Inc., founded in 2010 by Solomon Hykes, who sought to simplify containerization for developers. By 2013, Docker released its open-source platform, which built on LXC but introduced a standardized API, a registry (Docker Hub), and a unified toolchain. This was the moment docker containers transitioned from a niche experiment to a mainstream tool.The adoption of docker containers was accelerated by the rise of microservices architecture in the mid-2010s. Traditional monolithic applications were difficult to scale and maintain, while microservices—small, independent services—required a way to package and deploy them efficiently. Docker containers provided the perfect solution: each microservice could run in its own docker container, isolated from others but able to communicate via APIs. This shift wasn’t just technical; it represented a cultural change in how teams approached software development, emphasizing modularity, scalability, and collaboration.
Core Mechanisms: How It Works
Under the hood, a docker container leverages several Linux kernel features to achieve isolation and resource management. The most critical of these is cgroups (control groups), which limits and monitors system resources like CPU, memory, and disk I/O assigned to the container. Another key component is namespaces, which provides process isolation by creating separate instances of system resources (e.g., PID, network, mount points). When a docker container is created, Docker combines these mechanisms to ensure that the container’s processes are isolated from the host and other containers.Table of Contents
- The Complete Overview of Docker Containers
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What is the difference between a Docker image and a Docker container?
- Q: Can a Docker container run on any operating system?
- Q: How do Docker containers improve security compared to traditional VMs?
- Q: What is Docker Swarm, and how does it relate to Kubernetes?
- Q: How can I optimize a Docker container for performance?
- Q: Are Docker containers suitable for stateful applications like databases?
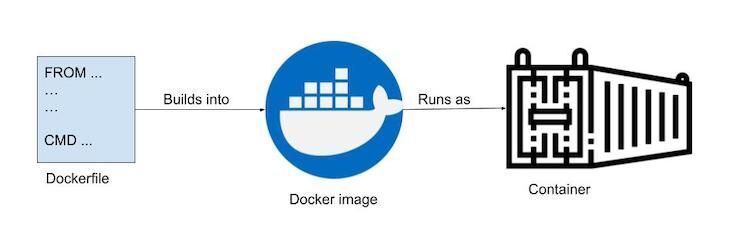
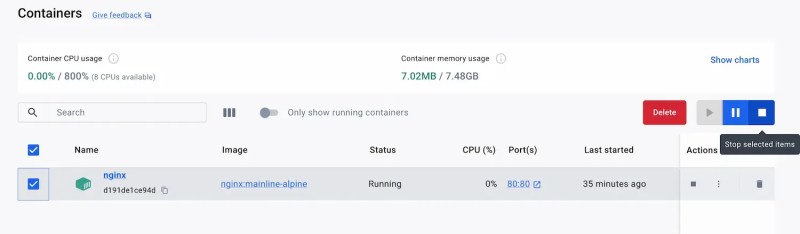
The lifecycle of a docker container begins with a Dockerfile, a script that defines the container’s environment, dependencies, and runtime configuration. When a developer runs `docker build`, Docker pulls base images (like `ubuntu` or `python:3.9`) from a registry, applies the instructions in the Dockerfile, and layers them to create a new image. This image is then used to instantiate one or more docker containers via `docker run`. Each container is essentially a running instance of the image, with its own filesystem, network stack, and process space. The beauty of this system is that multiple containers can share the same image, but each operates independently, allowing for efficient resource utilization and rapid scaling.
Key Benefits and Crucial Impact
The adoption of docker containers hasn’t just been a technical upgrade—it’s been a strategic imperative for organizations seeking agility in a fast-moving digital landscape. By eliminating environment inconsistencies, docker containers reduce the time spent debugging deployment issues, allowing teams to focus on innovation rather than infrastructure. They also enable infrastructure as code, where environments are defined in version-controlled files rather than manually configured servers. This shift has been particularly transformative for DevOps teams, who now treat docker containers as the standard unit of deployment, much like how developers once treated source code.The impact extends beyond development teams. Operations teams benefit from the portability of docker containers, which can run on-premises, in the cloud, or in hybrid environments without modification. This portability has fueled the growth of container orchestration platforms like Kubernetes, which manage clusters of docker containers at scale. For businesses, the result is reduced operational overhead, faster time-to-market, and the ability to scale applications dynamically in response to demand.
> "Docker didn’t just change how we deploy software; it changed how we think about software itself. Containers are the missing link between code and infrastructure, bridging the gap that has long separated developers and operations." — Solomon Hykes, Founder of Docker Inc.
Major Advantages
- Consistency Across Environments: A docker container ensures that the application runs the same way in development, testing, and production, eliminating the "works on my machine" problem.
- Resource Efficiency: Unlike VMs, docker containers share the host OS kernel, reducing overhead and improving performance, especially in cloud environments.
- Portability: Docker containers can be deployed anywhere—on a local machine, a cloud provider, or a bare-metal server—without requiring changes to the application or its dependencies.
- Isolation and Security: Each docker container operates in its own isolated environment, reducing the risk of conflicts between applications and enhancing security through minimal attack surfaces.
- Scalability: Docker containers can be spun up or torn down in seconds, making them ideal for microservices architectures and auto-scaling workloads.
Comparative Analysis
| Docker Containers | Virtual Machines (VMs) |
|---|---|
|
|
|
|
|
|
Future Trends and Innovations
The evolution of docker containers is far from over. One of the most significant trends is the integration of serverless computing, where docker containers are used to run ephemeral, event-driven workloads without managing servers. Platforms like AWS Fargate and Google Cloud Run are already leveraging docker containers to provide serverless container execution, reducing operational complexity for developers. Additionally, the rise of WebAssembly (Wasm) is introducing a new layer of abstraction that could further optimize docker containers, allowing them to run not just on Linux but across multiple operating systems and even in browsers.Another frontier is edge computing, where docker containers are being deployed on IoT devices and edge servers to process data locally, reducing latency and bandwidth usage. As 5G and IoT proliferate, the ability to run lightweight, portable docker containers at the edge will become increasingly critical. Meanwhile, advancements in container security—such as improved image scanning, runtime protection, and zero-trust architectures—are addressing the growing concerns around containerized environments. The future of docker containers will likely be defined by their ability to adapt to these emerging paradigms while maintaining their core strengths: efficiency, portability, and scalability.

Conclusion
The docker container is more than a tool—it’s a philosophy that challenges the status quo of software deployment. By encapsulating applications and their dependencies into portable, isolated units, docker containers have dismantled the barriers between development and operations, enabling teams to build, test, and deploy software with unprecedented speed and reliability. This shift hasn’t just improved workflows; it’s redefined the boundaries of what’s possible in cloud-native development.As the technology continues to evolve, the influence of docker containers will extend beyond traditional IT environments into edge computing, serverless architectures, and even consumer devices. The key to harnessing this power lies in understanding not just how docker containers work, but how they reshape the way we think about software infrastructure. For developers, operators, and architects alike, the docker container isn’t just a part of the toolchain—it’s the foundation of the future.
Comprehensive FAQs
Q: What is the difference between a Docker image and a Docker container?
A: A Docker image is a static, immutable template that defines the environment and dependencies of an application. It’s built from a Dockerfile and stored in a registry (like Docker Hub). A docker container, on the other hand, is a running instance of that image. Think of an image as a blueprint and a container as the actual house built from that blueprint.
Q: Can a Docker container run on any operating system?
A: Docker containers are primarily designed to run on Linux due to their reliance on Linux kernel features like namespaces and cgroups. However, Docker Desktop provides a lightweight Linux VM on macOS and Windows, allowing docker containers to run on those platforms. For production environments, Linux is still the recommended host OS for optimal performance and compatibility.
Q: How do Docker containers improve security compared to traditional VMs?
A: Docker containers enhance security by running applications in isolated environments with minimal privileges. Since they share the host OS kernel, they have a smaller attack surface than VMs, which require a full guest OS. Additionally, Docker provides features like user namespaces, seccomp, and AppArmor to further restrict container capabilities. However, security still depends on proper configuration—misconfigured containers can pose risks, such as privilege escalation or image vulnerabilities.
Q: What is Docker Swarm, and how does it relate to Kubernetes?
A: Docker Swarm is Docker’s built-in container orchestration tool that allows docker containers to be deployed and managed across a cluster of nodes. It provides features like load balancing, scaling, and rolling updates. Kubernetes, while more complex and feature-rich, serves a similar purpose but is designed for larger-scale deployments. Many organizations use Kubernetes alongside Docker (or other container runtimes) for production-grade orchestration, while Docker Swarm is often used for simpler, Docker-centric setups.
Q: How can I optimize a Docker container for performance?
A: Optimizing a docker container involves several best practices:
- Use multi-stage builds in Dockerfiles to reduce final image size by discarding build-time dependencies.
- Choose lightweight base images (e.g., `alpine` instead of `ubuntu`).
- Minimize layers in the Dockerfile to speed up builds.
- Enable Docker’s build cache to reuse layers across builds.
- Monitor container resource usage (CPU, memory) and adjust limits as needed.
Q: Are Docker containers suitable for stateful applications like databases?
A: While docker containers are excellent for stateless applications, they require careful handling for stateful workloads like databases. The challenge lies in data persistence—containers are ephemeral by design, so data stored inside a container is lost when it’s removed. Solutions include:
- Using volumes or bind mounts to store data on the host filesystem.
- Leveraging external storage systems (e.g., cloud storage, network-attached storage).
- Implementing database replication or backups to ensure data durability.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Bevvy.