What Are the Three Main Goals of Data Lifecycle Management (DLM)? The Hidden Blueprint for Strategic Data Mastery
Data isn’t static—it evolves, degrades, and demands intentional stewardship. Organizations that treat it as a passive asset risk regulatory fines, operational inefficiencies, and lost competitive edge. The question isn’t whether to manage data’s lifecycle, but how to align its journey with business objectives. The answer lies in understanding what are the three main goals of data lifecycle management (DLM)?—a framework that transcends mere storage to ensure data remains reliable, compliant, and strategically valuable at every stage.
Most companies focus on acquisition or analysis, but the real leverage comes from governing data’s entire existence: from creation to archival. DLM isn’t a one-size-fits-all solution; it’s a dynamic process that adapts to industry regulations, technological shifts, and evolving business needs. Without it, even the most sophisticated analytics tools become useless when fed corrupted or non-compliant data. The stakes are higher than ever—GDPR, CCPA, and sector-specific mandates (like HIPAA for healthcare) enforce penalties that can cripple organizations. Yet, many still operate in the dark, unaware that their data’s lifecycle is silently undermining their growth.
The three pillars of DLM—preservation, optimization, and compliance—aren’t just technical requirements. They’re the difference between data as a liability and data as a strategic weapon. This framework ensures that every byte of information serves a purpose, whether it’s powering AI models, satisfying auditors, or enabling real-time decision-making. Ignoring DLM is like building a skyscraper without a foundation: the structure may stand for a while, but the cracks will eventually collapse under pressure.

The Complete Overview of Data Lifecycle Management (DLM)
Data Lifecycle Management (DLM) is the disciplined approach to overseeing data through its entire existence—from inception to obsolescence. Unlike traditional data management, which often treats storage as an afterthought, DLM integrates technical, legal, and business processes to ensure data remains accurate, accessible, and actionable. The three core goals—what are the three main goals of data lifecycle management (DLM)?—are not arbitrary; they address the most critical pain points in modern enterprises: data decay, regulatory exposure, and wasted resources. Without DLM, organizations risk drowning in siloed datasets, non-compliant archives, and inefficiencies that inflate costs by up to 30% (Gartner, 2023).The misconception that DLM is solely an IT concern is a recipe for failure. In reality, it’s a cross-functional imperative that aligns with finance (cost reduction), legal (risk mitigation), and operations (process efficiency). For example, a retail giant might use DLM to purge outdated customer transaction records—saving storage costs—while ensuring compliance with privacy laws. The same framework can later repurpose that data for predictive analytics, turning a compliance burden into a revenue driver. This duality is why DLM is increasingly becoming a board-level discussion, not just a back-office function.
Historical Background and Evolution
The origins of DLM trace back to the 1980s, when enterprises first grappled with the exponential growth of digital records. Early solutions focused on data archiving—a reactive approach to storing information until it was no longer needed. However, as regulations like the EU’s Data Protection Directive (1995 precursor to GDPR) emerged, the focus shifted toward retention policies and legal holds. Companies realized that simply storing data wasn’t enough; they needed to classify, secure, and eventually dispose of it in a way that met both business and legal requirements.The 2000s marked a turning point with the rise of enterprise content management (ECM) systems, which integrated DLM principles into workflows. But it wasn’t until the 2010s—with the explosion of unstructured data (emails, IoT sensors, social media)—that DLM evolved into a strategic discipline. Cloud computing and AI further complicated the landscape, demanding dynamic policies that could adapt to data’s velocity, variety, and veracity. Today, DLM is no longer optional; it’s a non-negotiable component of digital transformation, especially in sectors like healthcare, finance, and government, where data’s lifecycle directly impacts public trust and regulatory survival.
Core Mechanisms: How It Works
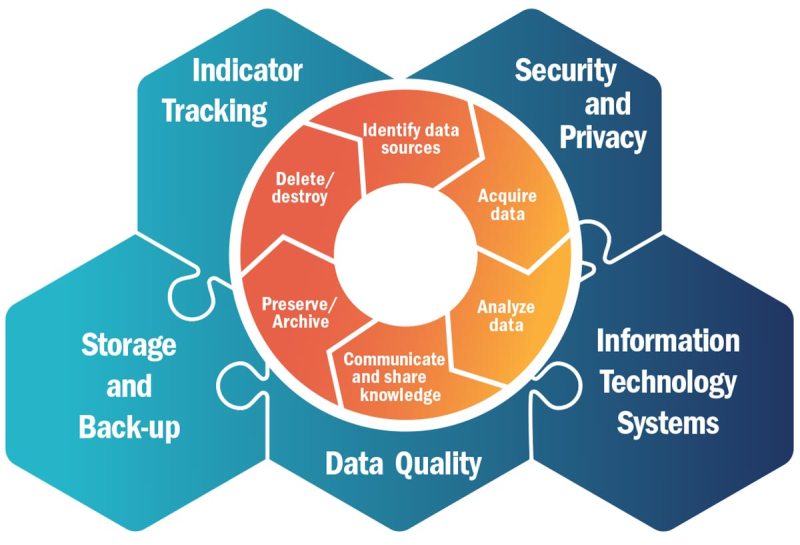
DLM operates through a structured framework that spans five key phases: creation, storage, usage, archival, and destruction. Each phase is governed by policies that ensure data meets the three primary objectives—what are the three main goals of data lifecycle management (DLM)?—without sacrificing agility. For instance, during the storage phase, data might be tiered based on access frequency (hot, warm, cold), while usage enforces role-based permissions to prevent unauthorized modifications. The archival stage often involves migration to cost-effective storage (e.g., AWS Glacier) with automated compliance checks, and destruction follows strict protocols to avoid legal exposure.Table of Contents
- The Complete Overview of Data Lifecycle Management (DLM)
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How does DLM differ from traditional data backup solutions?
- Q: Can small businesses benefit from DLM, or is it only for enterprises?
- Q: What industries have the most stringent DLM requirements?
- Q: How does AI enhance DLM?
- Q: What’s the biggest misconception about DLM?
- Q: Can DLM help with data monetization?
- Q: What happens if an organization ignores DLM?
The mechanics behind DLM are powered by a combination of automation, metadata tagging, and governance tools. For example, a healthcare provider might use DLM to automatically flag patient records for retention based on HIPAA’s 6-year rule, while financial institutions apply SEC-mandated policies to trading data. The system doesn’t just react to data—it anticipates its behavior. Machine learning models can now predict data decay patterns, allowing proactive cleanup before compliance risks materialize. This predictive capability is what sets modern DLM apart from its static predecessors.
Key Benefits and Crucial Impact
The impact of DLM extends far beyond compliance checklists. Organizations that implement it see measurable improvements in cost efficiency, risk reduction, and operational agility. A 2022 study by IDC found that companies with mature DLM strategies reduced storage costs by 40% while improving data retrieval speeds by 60%. The reason? DLM eliminates redundant copies, automates tiering, and ensures only relevant data remains active. More importantly, it transforms data from a cost center into a profit driver—enabling analytics, AI training, and customer personalization without the overhead of managing obsolete or unstructured datasets.The strategic value of DLM becomes even clearer when considering its role in mergers and acquisitions (M&A). During due diligence, buyers scrutinize a target company’s data governance—poor DLM can lead to acquisition failures worth billions. For instance, a tech firm acquiring a healthcare provider might discover that patient records are scattered across ungoverned systems, creating legal liabilities. DLM mitigates these risks by providing auditable trails, ensuring data integrity, and accelerating integration. In an era where data is often called the "new oil," DLM is the refinery that turns raw information into fuel for innovation.
"Data lifecycle management isn’t about storing data—it’s about orchestrating its death, rebirth, and legacy in a way that aligns with business and regulatory demands." — Dr. Emily Carter, Chief Data Officer, Deloitte Consulting
Major Advantages
- Cost Optimization: DLM reduces storage expenses by up to 50% through automated tiering, compression, and deletion of obsolete data. For example, a global bank using DLM saved $12M annually by retiring redundant transaction logs.
- Regulatory Compliance: Automated retention policies ensure adherence to laws like GDPR, CCPA, and SOX, reducing fines and legal exposure. A European retailer avoided a €50M GDPR penalty by using DLM to purge customer data per "right to erasure" requests.
- Enhanced Security: By classifying data sensitivity, DLM limits attack surfaces. A healthcare DLM system blocked a ransomware attempt by encrypting only high-risk patient records, preventing a $10M breach.
- Operational Efficiency: Self-service data access via DLM reduces IT bottlenecks. A manufacturing firm cut data retrieval times from days to minutes by implementing role-based DLM policies.
- Strategic Insights: DLM enables data repurposing—e.g., converting archived logs into training datasets for predictive maintenance models, adding $8M in annual savings for an energy company.
Comparative Analysis
| Aspect | Traditional Data Management | Data Lifecycle Management (DLM) |
|---|---|---|
| Focus | Storage and backup | End-to-end data governance (creation to destruction) |
| Compliance Handling | Manual audits, reactive fixes | Automated policy enforcement, real-time monitoring |
| Cost Impact | High due to siloed storage and redundant copies | Low via tiered storage and intelligent archival |
| Business Value | Limited to operational continuity | Enables analytics, AI, and revenue-generating use cases |
Future Trends and Innovations
The next frontier of DLM lies in AI-driven automation and quantum-resistant encryption. Current DLM systems rely on rule-based policies, but emerging tools like generative AI will dynamically adjust retention schedules based on predicted business needs. For instance, a DLM platform might automatically extend the lifecycle of supply chain data if an AI model detects a looming shortage. Meanwhile, zero-trust architectures will integrate with DLM to ensure data is only accessible to verified entities, even during its archival phase.Another disruptive trend is decentralized DLM, where blockchain-like ledgers track data provenance across hybrid cloud environments. This would solve the "black box" problem in multi-cloud setups, where organizations struggle to prove data integrity during audits. As regulations like the EU’s Digital Operational Resilience Act (DORA) tighten, DLM will also embed resilience testing—simulating cyberattacks to identify vulnerabilities in data retention policies. The future of DLM isn’t just about managing data; it’s about future-proofing it against unknown risks.

Conclusion
The three goals of what are the three main goals of data lifecycle management (DLM)?—preservation, optimization, and compliance—are the bedrock of modern data strategy. They address the twin challenges of data proliferation and regulatory complexity, ensuring that organizations don’t just survive but thrive in the data economy. The companies that treat DLM as an afterthought will face escalating costs, compliance nightmares, and lost opportunities. Conversely, those that embed DLM into their DNA will unlock new revenue streams, mitigate risks, and gain a competitive edge.The question isn’t if your data needs lifecycle management—it’s how soon you’ll implement it before outdated processes become a liability. DLM isn’t a project; it’s a continuous evolution, one that demands investment today for exponential returns tomorrow. In an era where data breaches cost $4.45M on average (IBM, 2023) and poor data quality drains $12.9M annually (Gartner), the cost of inaction is far higher than the cost of action.
Comprehensive FAQs
Q: How does DLM differ from traditional data backup solutions?
DLM is proactive and policy-driven, governing data from creation to destruction, while traditional backups are reactive, focusing only on recovery. DLM includes compliance, optimization, and strategic repurposing—backup systems lack these layers.
Q: Can small businesses benefit from DLM, or is it only for enterprises?
DLM’s principles scale. Small businesses can start with automated retention policies (e.g., deleting old invoices after 7 years) and grow into full lifecycle governance as they expand. Cloud-based DLM tools (like AWS Data Lifecycle Manager) offer cost-effective entry points.
Q: What industries have the most stringent DLM requirements?
Healthcare (HIPAA), finance (SEC, Basel III), and government (FOIA) sectors demand rigorous DLM due to high compliance stakes. Even retail now faces DLM pressures from GDPR’s "right to erasure" and CCPA’s data minimization rules.
Q: How does AI enhance DLM?
AI automates classification, predicts data decay, and adjusts retention policies dynamically. For example, an AI model might flag outdated product catalogs for archival while extending lifecycles for high-value customer interaction data.
Q: What’s the biggest misconception about DLM?
The belief that DLM is solely an IT problem. In reality, it requires collaboration between legal, finance, and operations teams to align policies with business goals—e.g., balancing compliance with data-driven innovation.
Q: Can DLM help with data monetization?
Absolutely. By ensuring data quality and compliance, DLM enables safe repurposing—e.g., anonymizing customer data for third-party analytics or training AI models. A telco used DLM to monetize archived call logs for predictive churn models.
Q: What happens if an organization ignores DLM?
Risks include regulatory fines (e.g., GDPR’s 4% of global revenue), data breaches from unsecured archives, and operational inefficiencies. A 2021 study found that 60% of data breaches involved unmanaged archival systems.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Bevvy.