How to Check Security Risks & Implement Protection Strategies in 2024
Cyber threats don’t announce themselves—they exploit weaknesses before you even realize they exist. A single overlooked vulnerability can lead to data breaches, financial losses, or operational paralysis. The gap between detection and exploitation is measured in minutes, not days. Yet most organizations still rely on reactive measures, leaving critical assets exposed to automated scans, insider threats, and zero-day attacks.
Effective security isn’t about installing the latest antivirus or slapping on a compliance badge. It’s about systematically checking security risks with precision, then implementing protection strategies that adapt faster than threats evolve. The difference between a breach and a bulletproof defense often comes down to how thoroughly you audit risks and how dynamically you respond.
This isn’t theoretical. In 2023 alone, ransomware attacks surged by 97%, while supply chain compromises accounted for 62% of critical breaches—proving that traditional perimeter defenses are obsolete. The question isn’t if you’ll face an attack, but when. The only variable you control is how well you’ve prepared to identify vulnerabilities before attackers do and how swiftly you can deploy countermeasures.
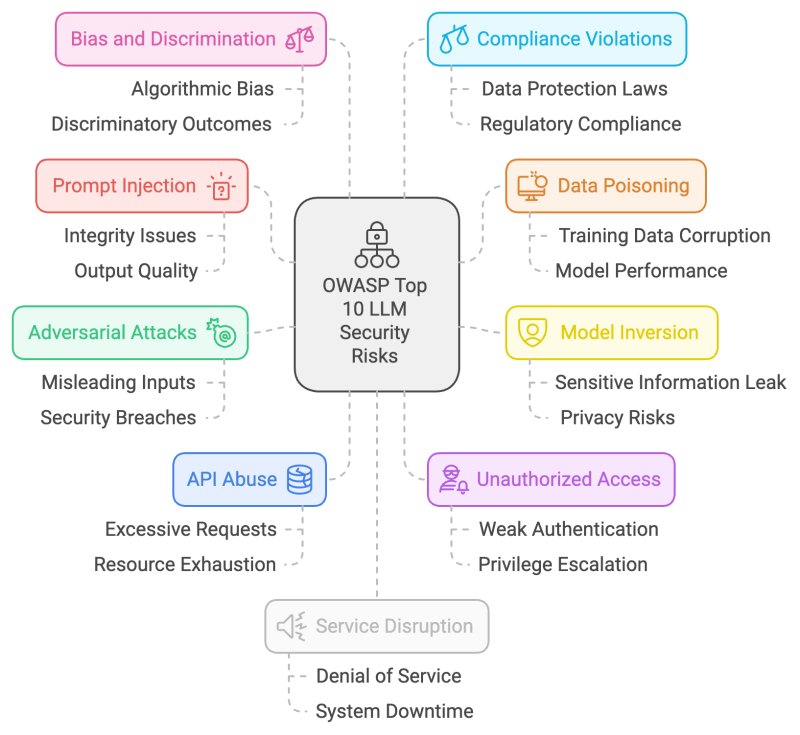
The Complete Overview of Checking Security Risks and Protection Strategies
Modern security risk assessment is a hybrid discipline, blending technical audits with behavioral analytics to uncover threats before they materialize. The process begins with continuous vulnerability scanning, where automated tools probe systems for known exploits, misconfigurations, and weak authentication protocols. But scanning alone is insufficient—it’s the foundation. The next layer involves threat modeling, where security teams map potential attack paths by simulating adversary tactics, techniques, and procedures (TTPs). This isn’t just about finding flaws; it’s about predicting how an attacker would exploit them.
Protection strategies, meanwhile, have shifted from static defenses to adaptive frameworks that integrate real-time threat intelligence, AI-driven anomaly detection, and automated response protocols. The most resilient organizations don’t just patch vulnerabilities—they harden systems against exploitation by combining preventive controls (like zero-trust architecture) with detective measures (such as SIEM correlation) and corrective actions (playbook-driven incident response). The goal isn’t perfection; it’s reducing the attack surface to a point where exploitation becomes prohibitively difficult.
Historical Background and Evolution
The concept of checking security risks traces back to the 1970s, when early computer security standards like the Orange Book introduced risk assessment as a structured discipline. However, these frameworks were static, relying on manual audits and checklists that couldn’t keep pace with the digital arms race. The turning point came in the 1990s with the rise of the internet, when organizations realized that security wasn’t just about physical access—it was about protecting data in motion and at rest. The NIST Risk Management Framework (RMF), published in 2002, formalized the process into a repeatable cycle: identify, protect, detect, respond, and recover.
Table of Contents
- The Complete Overview of Checking Security Risks and Protection Strategies
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How often should organizations conduct security risk assessments?
- Q: What’s the difference between a vulnerability scan and a penetration test?
- Q: Can small businesses afford robust security protection strategies?
- Q: How do zero-trust models improve security risk protection?
- Q: What’s the most common mistake organizations make in security risk management?
Today, the evolution has accelerated with the cloud, IoT, and AI. Traditional vulnerability scanners now integrate with continuous monitoring platforms that ingest data from endpoints, networks, and third-party feeds. Protection strategies have similarly transformed: firewalls and VPNs are no longer sufficient. Instead, organizations deploy deception technology (honeypots), behavioral AI for endpoint detection, and micro-segmentation to contain breaches. The shift from reactive to proactive security isn’t optional—it’s a survival tactic in an era where attackers operate with surgical precision.
Core Mechanisms: How It Works
At its core, checking security risks involves three interdependent mechanisms: discovery, analysis, and mitigation. Discovery begins with asset inventory—cataloging every device, application, and data repository across the organization. Tools like Nessus or OpenVAS automate this by scanning for outdated software, default credentials, and exposed ports. But discovery alone misses context. Analysis requires correlating these findings with threat intelligence feeds (e.g., MITRE ATT&CK) to assess exploitability and business impact. For example, a misconfigured S3 bucket might seem minor until you realize it contains customer PII—then it becomes a critical risk.
Protection strategies are equally layered. Preventive controls (e.g., encryption, least-privilege access) reduce the attack surface, while detective controls (e.g., UEBA, log analysis) provide visibility into suspicious activity. The most effective approaches combine these with automated response—for instance, isolating a compromised host or revoking API keys in real time. The key is defense in depth: no single layer should be the sole barrier. If one fails, the next must compensate. This is why organizations now adopt frameworks like CIS Controls or ISO 27001, which provide prescriptive guidance for risk mitigation.
Key Benefits and Crucial Impact
Implementing robust security risk protection strategies isn’t just a checkbox for compliance—it’s a competitive advantage. Organizations that proactively check security risks reduce downtime, avoid regulatory fines (average cost: $4.45 million per breach), and preserve customer trust. The financial stakes are clear, but the intangible benefits are equally critical: a culture of security awareness, faster incident response, and the ability to innovate without fear of exploitation. In industries like healthcare or finance, where data is a liability, these strategies aren’t optional—they’re table stakes.
Yet the impact extends beyond the balance sheet. High-profile breaches (e.g., SolarWinds, Colonial Pipeline) have demonstrated that security failures can destabilize entire sectors. By contrast, organizations that embed risk assessment into their DNA—from development (DevSecOps) to operations—gain resilience. They recover faster, maintain operational continuity, and even turn security into a differentiator. For example, a fintech firm that detects and mitigates threats before they escalate can outmaneuver competitors in a cyber arms race.
"Security isn’t a product, a thing, or even a department. If information is the oil of the 21st century, then security is the refining process—continuous, adaptive, and essential to survival."
— Bruce Schneier, Security Technologist
Major Advantages
- Reduced Exposure Surface: Systematic security risk checks identify and remediate vulnerabilities before attackers exploit them, minimizing the attack surface.
- Regulatory Compliance: Frameworks like GDPR, HIPAA, or PCI DSS mandate risk assessments—proactive strategies ensure compliance and avoid penalties.
- Cost Efficiency: The average cost of a data breach is $4.45M; investing in prevention (e.g., $150K/year for a SIEM) saves millions in recovery and reputational damage.
- Operational Resilience: Automated protection strategies (e.g., SOAR) reduce mean time to detect (MTTD) and contain incidents within hours, not days.
- Strategic Trust: Customers and partners increasingly prioritize security posture—organizations that demonstrate rigorous risk protection gain a competitive edge.

Comparative Analysis
| Aspect | Traditional Approach | Modern Protection Strategies |
|---|---|---|
| Risk Assessment Frequency | Quarterly/annual audits | Continuous, real-time monitoring |
| Detection Capabilities | Signature-based (known threats) | Behavioral AI + threat intelligence |
| Response Time | Manual, hours/days | Automated, minutes |
| Attack Surface Coverage | Perimeter-focused (firewalls, VPNs) | Zero-trust, micro-segmentation, cloud-native |
Future Trends and Innovations
The next frontier in security risk protection lies in hyper-automation and predictive analytics. Current tools rely on historical data, but emerging AI models (like GPT-4 for security) are now capable of generating synthetic attack scenarios to stress-test defenses. This shift from reactive to predictive security will redefine risk assessment, allowing organizations to simulate breaches before they occur. Similarly, quantum-resistant cryptography is becoming a priority as quantum computing threatens to break RSA and ECC encryption—organizations must start transitioning to post-quantum algorithms like Lattice-based cryptography.
Another critical trend is the convergence of physical and digital security. As IoT devices proliferate, the attack surface expands into OT (Operational Technology) environments—think smart grids, manufacturing systems, or healthcare devices. Protection strategies will need to integrate OT security with IT, using unified threat intelligence and cross-domain incident response. The future belongs to organizations that treat security as a dynamic, data-driven discipline—not a static checklist.
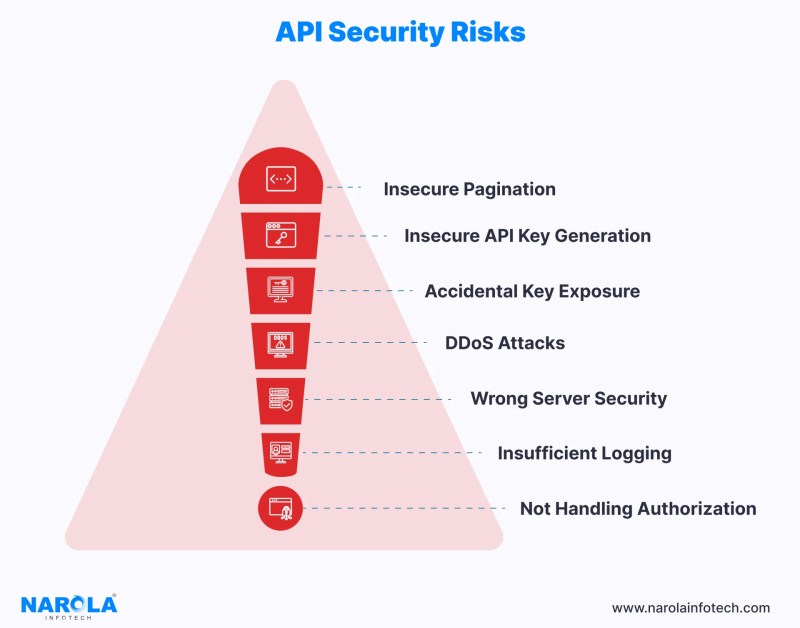
Conclusion
Checking security risks and deploying protection strategies isn’t a one-time project; it’s an ongoing discipline that demands rigor, adaptability, and integration across all business functions. The organizations that thrive in this landscape are those that treat security as a strategic imperative, not an afterthought. They invest in continuous risk assessment, automate response protocols, and foster a culture where every employee understands their role in defense. The alternative—reacting to breaches—is no longer sustainable.
As threats grow more sophisticated, the tools and frameworks will evolve, but the core principle remains unchanged: proactive protection is cheaper, faster, and more effective than recovery. The question for leaders isn’t whether to implement these strategies, but how aggressively to adopt them before the next wave of attacks renders outdated defenses useless.
Comprehensive FAQs
Q: How often should organizations conduct security risk assessments?
A: Continuous monitoring is ideal, but at minimum, organizations should perform quarterly vulnerability scans and annual penetration tests. Critical systems (e.g., payment processing, healthcare records) may require monthly assessments. Compliance mandates (e.g., PCI DSS) often dictate specific frequencies.
Q: What’s the difference between a vulnerability scan and a penetration test?
A: A vulnerability scan is automated and identifies potential weaknesses (e.g., outdated software, open ports). A penetration test (or pen test) is a manual, ethical hacking exercise that simulates real attacks to exploit vulnerabilities and assess actual risk. Scans are preventive; pen tests are validation.
Q: Can small businesses afford robust security protection strategies?
A: Yes, but prioritization is key. Small businesses should start with essential protections: multi-factor authentication (MFA), endpoint detection (EDR), and regular backups. Managed security services (MSSPs) offer scalable solutions at lower costs than in-house teams. The goal is to reduce risk to an acceptable level, not achieve 100% security.
Q: How do zero-trust models improve security risk protection?
A: Zero-trust eliminates the assumption that entities inside the network are safe. Instead, it enforces least-privilege access, continuous authentication, and micro-segmentation. This limits lateral movement if an attacker breaches one segment, containing the threat. It’s particularly effective against insider threats and supply chain attacks.
Q: What’s the most common mistake organizations make in security risk management?
A: Treating security as a siloed IT function rather than a business-wide responsibility. Many organizations focus on technical controls (e.g., firewalls) while neglecting human factors (phishing training) or third-party risks (vendor security). Effective risk protection requires alignment across departments, from HR to procurement.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Bevvy.