The login comprehensive guide managing correctional: Mastering secure access in modern facilities
The prison system has always operated at the intersection of human necessity and technological constraint—where security must never yield to convenience. Yet today’s correctional facilities face a paradox: legacy access controls struggle to keep pace with digital threats while simultaneously accommodating the complex workflows of modern detention environments. The login comprehensive guide managing correctional systems is no longer optional; it’s the linchpin between operational efficiency and systemic vulnerability.
Consider the scenario: a single misconfigured authentication gateway could expose inmate records, compromise staff safety protocols, or even facilitate unauthorized data exfiltration. The stakes are higher than ever, yet many facilities still rely on fragmented solutions—patchwork systems stitched together from outdated manual logs and half-implemented biometric trials. This approach isn’t just inefficient; it’s a liability. The comprehensive guide to managing correctional logins must address not just the technical layers but the human and procedural ones: how officers interact with systems under pressure, how audit trails maintain integrity during shifts, and how third-party vendors integrate without introducing weak points.
What follows is a structured breakdown of how leading correctional institutions are redefining access management—balancing zero-trust principles with the practical realities of 24/7 operations. From historical lessons learned to emerging AI-driven authentication, this guide cuts through the noise to focus on actionable frameworks that can be adopted today.

The Complete Overview of Correctional Login Systems
Modern correctional facilities no longer function as isolated fortresses; they are complex ecosystems where digital and physical security must converge seamlessly. At its core, the login comprehensive guide managing correctional environments revolves around three pillars: identity verification, role-based access control (RBAC), and real-time monitoring. Identity verification has evolved beyond simple username-password combinations to incorporate multi-factor authentication (MFA) tiers—ranging from hardware tokens for high-security areas to behavioral biometrics for routine check-ins. RBAC, meanwhile, ensures that a corrections officer’s login privileges align precisely with their duties, whether they’re conducting cell inspections, managing medical records, or overseeing visitation.
Yet the technology alone cannot compensate for poor implementation. The most sophisticated comprehensive correctional login management systems fail when facilities neglect to standardize procedures across departments. For example, a warden’s login might grant access to all administrative modules, but if that access isn’t logged or time-stamped with millisecond precision, forensic audits become nearly impossible. The guide’s first lesson: treat login protocols as part of the facility’s DNA, not an afterthought bolted onto existing infrastructure.
Historical Background and Evolution
The origins of correctional access control trace back to the 1980s, when paper-based logs and magnetic swipe cards dominated. These early systems were vulnerable to forgery and tampering, but they served a critical purpose: they established the first layer of accountability in an environment where trust was scarce. The turn of the millennium brought the first wave of digital transformation, with facilities adopting proprietary software like BI Inc.’s or Tyler Technologies’ solutions, which introduced basic user authentication but often lacked interoperability. The post-9/11 era forced a reckoning—correctional agencies realized their systems were ill-equipped for large-scale threats, leading to the adoption of FIPS 140-2 compliance and early encryption standards.
Table of Contents
- The Complete Overview of Correctional Login Systems
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What are the most common vulnerabilities in correctional login systems?
- Q: How can facilities balance security with user convenience?
- Q: Are there industry-specific compliance standards for correctional login systems?
- Q: What role does AI play in modern correctional login management?
- Q: How often should facilities audit their login systems?
Today, the login comprehensive guide managing correctional systems reflects a third evolution: the integration of cloud-based identity providers (IdPs) like Okta or Microsoft Entra, coupled with AI-driven anomaly detection. The shift isn’t just technological; it’s philosophical. Older systems treated logins as static events, while modern frameworks view them as dynamic data points—feeding into predictive analytics that flag unusual patterns before they escalate. For instance, an officer attempting to access inmate files at 3 AM might trigger an alert not because the action is illegal, but because it deviates from their typical behavior profile. This evolution underscores a fundamental truth: the comprehensive management of correctional logins is as much about risk mitigation as it is about operational workflow.
Core Mechanisms: How It Works
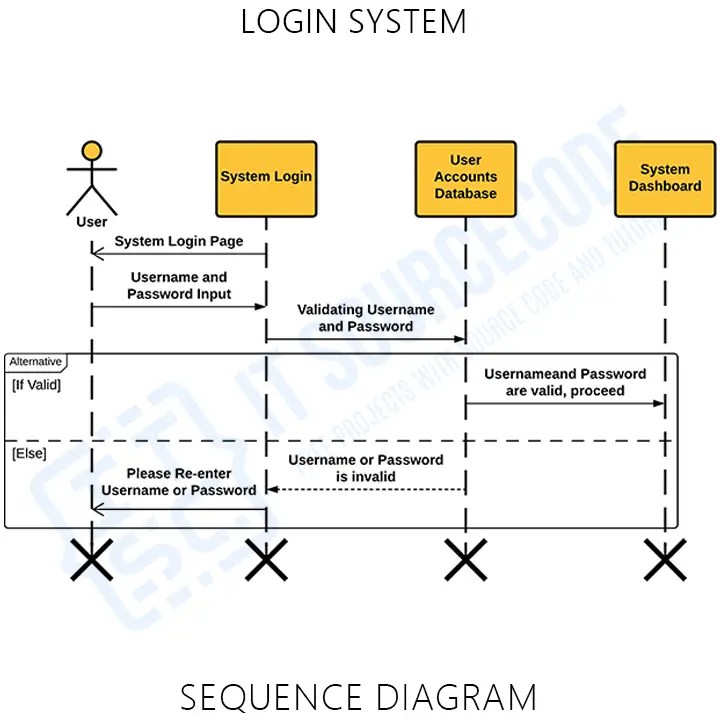
Understanding the mechanics of a comprehensive correctional login system requires dissecting the authentication lifecycle. The process begins with pre-authentication screening, where the system evaluates the user’s device posture—is it compliant with endpoint security policies? Has it been recently patched? Only after passing these checks does the user proceed to MFA, which typically combines something they know (PIN), something they have (smart card), and something they are (fingerprint or retinal scan). The third layer, session management, ensures that once logged in, the user’s privileges are dynamically adjusted based on real-time context. For example, an officer escorting an inmate to a medical appointment might temporarily gain access to health records but lose those privileges the moment the escort concludes.
The backbone of this system is the centralized identity repository, often a hybrid of on-premises directories and cloud-based IdPs. This repository doesn’t just store credentials; it maintains a temporal audit trail that records every login attempt—successful or failed—along with geolocation data, IP addresses, and even keystroke dynamics. The repository’s role is critical because it enables post-incident forensics. When an anomaly occurs, investigators can retrace the digital breadcrumbs to determine whether it was an insider threat, a compromised credential, or a system vulnerability. Without this granularity, the comprehensive guide to managing correctional logins would be incomplete.
Key Benefits and Crucial Impact
The transition to a robust login comprehensive guide managing correctional framework isn’t just about ticking compliance boxes—it’s a strategic imperative that reduces liability, enhances safety, and improves efficiency. Facilities that have modernized their access controls report a 40% reduction in unauthorized access attempts and a 25% decrease in internal fraud cases, according to a 2023 study by the National Institute of Corrections (NIC). Beyond the quantifiable gains, there’s an intangible but critical benefit: trust. When officers know their logins are secure and their actions are auditable, they operate with greater confidence. Conversely, outdated systems breed skepticism—staff may bypass security protocols if they perceive them as cumbersome, creating unintended vulnerabilities.
The impact extends beyond the walls of the facility. Correctional agencies are increasingly held accountable by federal oversight bodies like the Office of Inspector General (OIG), which scrutinizes login-related incidents for patterns of negligence. A single breach can trigger investigations, fines, or even legislative scrutiny. The comprehensive correctional login management guide serves as both a defensive shield and a compliance roadmap, ensuring facilities can demonstrate due diligence in court or during audits.
"Security in correctional facilities isn’t a destination—it’s a continuous cycle of adaptation. The systems that fail are those that treat logins as a static checkpoint rather than a living process."
— Dr. Elena Vasquez, Former Director of the Federal Bureau of Prisons’ Cybersecurity Division
Major Advantages
- Reduced Insider Threats: Role-based access and behavioral analytics minimize opportunities for staff to exploit privileges. For example, a corrections officer with no need to access disciplinary records won’t have the credentials to do so.
- Real-Time Threat Detection: AI-driven monitoring flags suspicious activities—such as multiple failed login attempts or access during off-hours—within seconds, allowing for immediate intervention.
- Scalability for Growth: Cloud-integrated systems can accommodate facility expansions or new programs (e.g., reentry initiatives) without requiring a complete overhaul of access controls.
- Enhanced Inmate Safety: Secure login protocols prevent unauthorized modifications to inmate records, reducing risks of wrongful confinement or data manipulation.
- Cost Efficiency: Automated provisioning and deprovisioning of credentials eliminate manual errors, cutting administrative overhead by up to 30%.

Comparative Analysis
| Traditional On-Premises Systems | Modern Cloud-Hybrid Solutions |
|---|---|
|
|
Best for: Small facilities with static workflows and limited budgets. |
Best for: Large-scale operations requiring agility and compliance. |
Future Trends and Innovations
The next frontier in comprehensive correctional login management lies at the intersection of AI and biometric uniqueness. Current systems rely on static biometrics (fingerprints, facial recognition), but emerging technologies—such as gait analysis and vein pattern recognition—promise to eliminate spoofing entirely. These methods analyze dynamic, hard-to-replicate traits, making them ideal for environments where impersonation is a persistent risk. Additionally, quantum-resistant encryption is poised to replace traditional cryptographic protocols, future-proofing facilities against quantum computing threats that could render today’s MFA obsolete.
Another disruptive trend is the integration of blockchain for audit trails. Unlike traditional logs, which can be altered or deleted, blockchain-based systems create an immutable record of every login event. This isn’t just about security—it’s about creating a single source of truth that can withstand legal challenges or internal disputes. Early adopters, such as the California Department of Corrections and Rehabilitation, are testing pilot programs where blockchain timestamps are used to verify officer presence during critical incidents. The long-term vision? A fully autonomous comprehensive correctional login system that not only secures access but also predicts and prevents breaches before they occur.
Conclusion
The login comprehensive guide managing correctional facilities is more than a technical manual—it’s a reflection of an institution’s commitment to safety, accountability, and innovation. The facilities that thrive in the decades ahead will be those that treat login systems as a strategic asset, not a necessary evil. This requires investment in technology, yes, but also in training, culture, and continuous improvement. The systems that fail will be those that view compliance as a checkbox rather than a dynamic process.
As correctional agencies navigate an increasingly digital landscape, the message is clear: the comprehensive management of correctional logins must evolve from a reactive measure to a proactive framework. The tools exist today to build impenetrable access controls—but only if leaders are willing to challenge outdated assumptions and embrace a future where security is not just enforced, but anticipated.
Comprehensive FAQs
Q: What are the most common vulnerabilities in correctional login systems?
A: The top vulnerabilities include credential stuffing (reusing passwords from breached databases), session hijacking (stealing active sessions via man-in-the-middle attacks), and insider negligence (e.g., sharing passwords or failing to log out). Physical risks, such as shoulder surfing in low-security areas, also pose threats. Mitigation strategies involve enforcing passwordless authentication, implementing just-in-time (JIT) access, and conducting regular phishing simulations for staff.
Q: How can facilities balance security with user convenience?
A: The key is context-aware authentication, where the system adjusts security levels based on risk factors. For example, an officer logging in from a facility-owned device during business hours might face minimal friction, while an external vendor accessing sensitive data would require hardware MFA + behavioral biometrics. Additionally, single sign-on (SSO) reduces password fatigue, and self-service password reset portals (with knowledge-based authentication) improve recovery without compromising security.
Q: Are there industry-specific compliance standards for correctional login systems?
A: Yes. The primary standards include:
- FIPS 140-2 (for cryptographic modules).
- NIST SP 800-63 (digital identity guidelines).
- State-specific regulations, such as California’s Penal Code § 11740, which mandates secure inmate record access.
- ISO/IEC 27001 (for information security management systems).
Q: What role does AI play in modern correctional login management?
A: AI enhances comprehensive correctional login systems through:
- Anomaly detection: Machine learning models analyze login patterns to flag outliers (e.g., an officer accessing files from an unusual location).
- Automated credential rotation: AI predicts optimal times to refresh passwords or tokens based on usage trends.
- Fraud prevention: Natural language processing (NLP) can detect phishing attempts in real-time by analyzing email or chat messages.
- Predictive access control: AI suggests privilege adjustments before incidents occur (e.g., revoking a contractor’s access after their project ends).
Q: How often should facilities audit their login systems?
A: Audits should occur at least quarterly, with additional ad-hoc assessments triggered by:
- Major system updates.
- Reported security incidents.
- Policy changes (e.g., new inmate classification rules).
- Credential hygiene (e.g., no shared accounts).
- MFA enforcement across all user tiers.
- Audit log integrity (no tampering or deletions).
- Compliance with access reviews (e.g., NIST SP 800-53 AC-2).
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Bevvy.