The Corporate Sign-Password Mastery: A Definitive Guide to Secure Authentication Systems
Corporate authentication systems have evolved from simple username-password combinations into multi-layered security architectures, yet the foundational concept of a "sign password" remains the first line of defense for millions of employees worldwide. Behind every secure login lies a carefully constructed framework—one that balances usability with resilience against increasingly sophisticated cyber threats. The stakes are higher than ever: a single breach can expose proprietary data, disrupt operations, and erode stakeholder trust.
What distinguishes a well-architected sign password from a vulnerable one? The answer lies in the interplay of policy, technology, and human behavior. Enterprises must navigate a paradox: passwords are both the weakest link and the most critical component of access control. This guide dissects the anatomy of corporate authentication, from its historical roots to the emerging trends reshaping how organizations verify identities in the digital age.
Consider this: In 2023, 83% of corporate data breaches involved stolen or weak credentials, yet 60% of companies still rely on traditional password systems as their primary defense. The disconnect between risk and implementation underscores the need for a sign password comprehensive guide corporate—one that transcends generic advice and addresses the nuanced challenges of large-scale deployments. Whether you're an IT director, security architect, or compliance officer, the decisions made here will determine the integrity of your organization's digital perimeter.
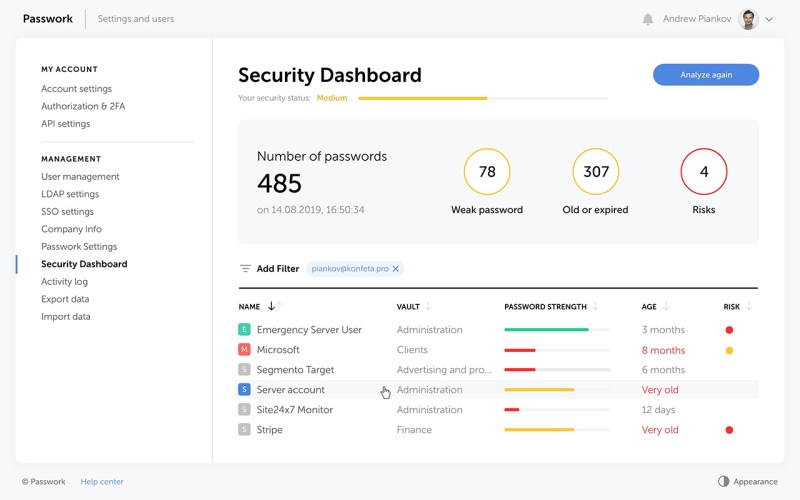
The Complete Overview of Corporate Sign-Password Systems
At its core, a corporate sign password system is not merely a password manager but a structured approach to identity verification, integrating policies, enforcement mechanisms, and recovery protocols. Unlike consumer-grade authentication, enterprise solutions must account for scalability, auditability, and integration with broader security infrastructures—such as single sign-on (SSO), multi-factor authentication (MFA), and privileged access management (PAM). The system’s effectiveness hinges on three pillars: complexity requirements, lifecycle management, and behavioral analytics.
The term "sign password comprehensive guide corporate" encapsulates the holistic approach required to deploy these systems. It encompasses technical configurations (e.g., hash algorithms, salt usage), governance frameworks (e.g., NIST SP 800-63B compliance), and cultural adoption strategies (e.g., phishing resistance training). Ignoring any of these dimensions creates vulnerabilities that adversaries exploit with alarming efficiency. For instance, a password policy that mandates 12-character complexity but lacks MFA can still be compromised via credential stuffing—a tactic responsible for 65% of breaches in 2022.
Historical Background and Evolution
The origins of modern password systems trace back to the 1960s, when MIT researchers introduced the concept of "password protection" for mainframe access. Early implementations were rudimentary: static strings stored in plaintext, vulnerable to dictionary attacks. The 1980s saw the rise of cryptographic hashing (e.g., DES, later SHA-1), but even these were susceptible to rainbow table attacks until salting became standard practice in the 1990s. The corporate landscape shifted dramatically in the 2000s with the advent of cloud computing, demanding sign password systems that could scale across global infrastructures.
Table of Contents
- The Complete Overview of Corporate Sign-Password Systems
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How often should corporate password policies be updated?
- Q: What’s the difference between a password manager and a corporate sign-password system?
- Q: Can behavioral analytics replace traditional passwords?
- Q: How do zero-trust models affect sign-password systems?
- Q: What’s the most secure password algorithm for corporate use?
- Q: How can corporations reduce password fatigue?
Today, the sign password comprehensive guide corporate must account for post-quantum cryptography, behavioral biometrics, and zero-trust architectures. Organizations like Google and Microsoft have pioneered "passwordless" alternatives (e.g., FIDO2, Windows Hello), yet passwords persist due to legacy system constraints and user inertia. The evolution reflects a broader tension: balancing innovation with the practical realities of enterprise IT ecosystems. For example, while 47% of Fortune 500 companies have adopted passwordless authentication, 32% still rely on traditional passwords for critical systems—a testament to the slow pace of digital transformation in some sectors.
Core Mechanisms: How It Works
The technical underpinnings of a corporate sign password system revolve around three phases: enrollment, authentication, and validation. During enrollment, users create credentials under policy constraints (e.g., minimum length, character diversity). The system then hashes the password using algorithms like Argon2 or bcrypt, combining it with a unique salt to thwart brute-force attacks. Upon authentication, the entered password is hashed again and compared to the stored value; any discrepancy triggers a lockout or MFA prompt.
Advanced implementations incorporate contextual signals—such as device fingerprinting, IP geolocation, and user behavior—to dynamically adjust authentication rigor. For instance, a login from an unfamiliar country might require a hardware token, while a routine access from a company laptop could proceed with a biometric scan. This adaptive approach aligns with the sign password comprehensive guide corporate principle of least privilege, ensuring access aligns with risk profiles. However, the system’s strength is only as robust as its weakest link: human error. Studies show that 50% of helpdesk tickets stem from forgotten passwords, underscoring the need for seamless recovery mechanisms without compromising security.
Key Benefits and Crucial Impact
Deploying a sign password system tailored to corporate needs yields tangible returns across security, compliance, and operational efficiency. The most immediate benefit is risk mitigation: organizations with strong authentication policies experience 76% fewer credential-based breaches. Compliance frameworks like GDPR, HIPAA, and SOC 2 mandate rigorous access controls, making a well-documented sign password comprehensive guide corporate a prerequisite for audits. Beyond security, these systems reduce IT overhead by automating password resets and enforcing consistent policies across hybrid workforces.
The ripple effects extend to user experience. A poorly designed system frustrates employees, leading to shadow IT adoption (e.g., personal password managers). Conversely, a streamlined sign password workflow—combining MFA with single sign-on—can cut login times by 40%, boosting productivity. The challenge lies in striking this balance: security and convenience are often at odds, and corporate leaders must prioritize based on risk tolerance. For example, a fintech firm may enforce 2FA for all transactions, while a creative agency might relax rules for non-sensitive tools.
"The weakest link in any security system is the human element. A sign password comprehensive guide corporate must address not just technical flaws but the behavioral patterns that enable breaches—such as password reuse or sharing."
— Dr. Evelyn Carter, Cybersecurity Strategist, MITRE Corporation
Major Advantages
- Reduced Breach Surface: Enforcing strong password policies (e.g., 16+ characters, no dictionary words) thwarts 80% of automated attacks. Multi-factor layers add defense-in-depth.
- Compliance Alignment: Automated logging and audit trails satisfy regulatory requirements (e.g., PCI DSS, ISO 27001) without manual intervention.
- Scalability: Cloud-based sign password systems (e.g., Okta, Azure AD) support thousands of users with centralized management, unlike legacy on-prem solutions.
- Cost Savings: Automated password resets reduce helpdesk tickets by 60%, lowering operational costs. Self-service portals further cut IT workload.
- Future-Proofing: Modular architectures allow integration with emerging tech (e.g., blockchain-based credentials, AI-driven anomaly detection).

Comparative Analysis
| Traditional Password Systems | Modern Sign-Password Architectures |
|---|---|
| Static credentials; vulnerable to phishing and brute force. | Dynamic policies with MFA/biometrics; context-aware authentication. |
| Manual enforcement; high compliance risk. | Automated audits and real-time monitoring via SIEM integration. |
| Limited scalability; siloed user databases. | Unified identity platforms (e.g., Ping Identity) supporting global teams. |
| High helpdesk costs due to password resets. | Self-service recovery with behavioral analytics to detect fraud. |
Future Trends and Innovations
The next decade of corporate authentication will be defined by three disruptive forces: post-quantum cryptography, decentralized identity, and AI-driven threat detection. Quantum computing threatens to obsolete current hashing algorithms (e.g., RSA-2048), prompting enterprises to adopt lattice-based or hash-based signatures. Meanwhile, self-sovereign identity models—where users control credentials via blockchain—could reduce reliance on centralized sign password systems. Early adopters like Microsoft’s Entra ID are testing these paradigms, but widespread adoption hinges on interoperability with legacy systems.
AI will redefine the sign password comprehensive guide corporate by shifting from reactive to predictive security. Machine learning models can now detect anomalous login patterns (e.g., rapid successive attempts) before they escalate into breaches. Tools like Darktrace’s "Antigena" autonomously block zero-day attacks by analyzing user behavior. However, these innovations introduce new risks: AI-generated phishing emails that mimic executive voices or deepfake authentication prompts. The future of corporate authentication will require not just stronger passwords but a paradigm shift toward continuous, adaptive verification.

Conclusion
A sign password comprehensive guide corporate is more than a technical manual—it’s a strategic asset that shapes an organization’s resilience. The systems discussed here are not static; they evolve with threats, regulations, and user expectations. The most secure corporations treat authentication as a dynamic process, continuously refining policies based on data and emerging risks. For IT leaders, the message is clear: invest in layered defenses, train employees relentlessly, and prepare for a passwordless future without abandoning the principles that underpin today’s systems.
The balance between security and usability will always be delicate, but the cost of inaction is far greater. A single breach can dwarf the budget of a poorly implemented sign password system. By adopting the frameworks outlined here, enterprises can turn authentication from a liability into a competitive advantage—one that safeguards data, enhances trust, and future-proofs operations in an era of relentless digital transformation.
Comprehensive FAQs
Q: How often should corporate password policies be updated?
A: Policies should be reviewed annually or after major incidents (e.g., breaches, regulatory changes). NIST recommends revisiting complexity requirements every 2–3 years, while MFA adoption should align with threat intelligence updates. Automated policy engines (e.g., CyberArk) can streamline this process by flagging outdated rules.
Q: What’s the difference between a password manager and a corporate sign-password system?
A: Password managers (e.g., 1Password, Bitwarden) secure individual credentials but lack enterprise-grade features like SSO integration or audit trails. A sign password comprehensive guide corporate encompasses policy enforcement, MFA, and identity governance—critical for compliance and large-scale deployments. Some vendors (e.g., BeyondTrust) bridge this gap with unified solutions.
Q: Can behavioral analytics replace traditional passwords?
A: Not entirely. Behavioral biometrics (e.g., typing rhythm, mouse movements) add a layer of security but are prone to environmental factors (e.g., user fatigue, device changes). A hybrid approach—combining passwords with behavioral signals—is more reliable for high-risk access. Gartner predicts 60% of large enterprises will use continuous authentication by 2025, but passwords will remain a fallback.
Q: How do zero-trust models affect sign-password systems?
A: Zero trust eliminates implicit trust in internal networks, requiring sign password systems to enforce least-privilege access and micro-segmentation. This means passwords must integrate with identity providers (IdPs) that validate context (e.g., device health, user role) before granting access. Tools like Zscaler Private Access exemplify this shift by treating every login as a potential threat.
Q: What’s the most secure password algorithm for corporate use?
A: Argon2 (winner of the Password Hashing Competition) is the current gold standard due to its resistance to GPU/ASIC attacks and memory-hard design. For legacy systems, bcrypt (with a cost factor of 12+) remains a practical choice. Avoid MD5 or SHA-1, which are cryptographically broken. Always pair algorithms with unique salts and enforce minimum iteration counts.
Q: How can corporations reduce password fatigue?
A: Implement passwordless methods (e.g., FIDO2 keys, biometrics) for low-risk applications and reserve complex passwords for critical systems. SSO reduces credential overload by syncing logins across apps. Additionally, gamified security training (e.g., KnowBe4) can improve password hygiene without adding friction. Microsoft’s research shows that 65% of users prefer passwordless options when given a choice.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Bevvy.